Discover the latest news and innovations from Fal.Con Europe Learn more


Your Cart
Added to Cart

There's nothing in your cart
per endpoint / per year
per endpoint / per month
×
![]()
Accelerate operations and boost threat detection
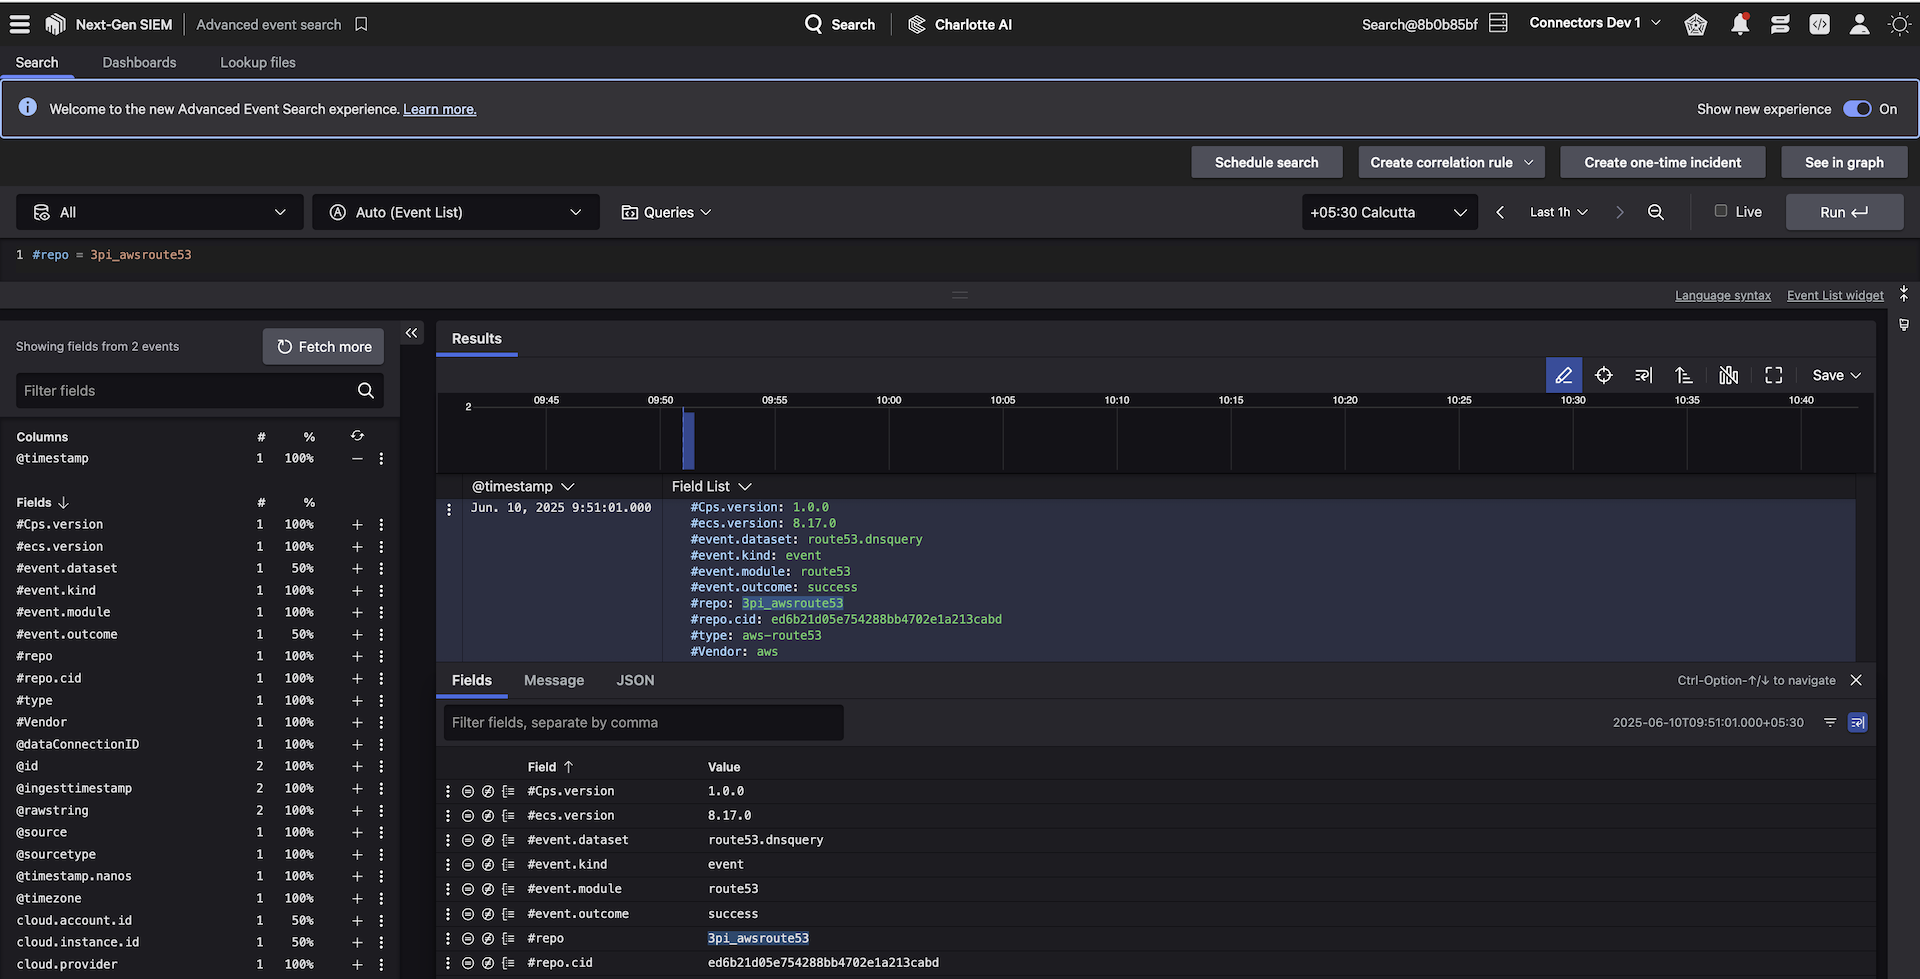
Secure your DNS infrastructure proactively and gain unified visibility by easily ingesting Amazon Route 53 DNS logs and events into the CrowdStrike Falcon® platform. By centralizing and correlating DNS activity data from Amazon Route 53, CrowdStrike, and additional third parties within CrowdStrike Falcon® Next-Gen SIEM, your team gains enhanced DNS-based threat detection, streamlined incident response, and an optimized security posture to ultimately protect against evolving cyber threats.
- Unify threat visibility in a single console
Save your analysts valuable time when investigating and triaging potential threats by minimizing context switching through CrowdStrike’s unified, threat-centric command console. - Simplify data ingestion
Easily ingest third party data with the new Falcon Data Connectors user interface. Get full visibility into your data ingestion pipeline and see all connectors with their corresponding status. - Improve threat hunting
Store and correlate your security data with other data sources leveraging the Falcon platform as a destination, including real-time detections and blazing-fast search to rapidly shut down threats.
Get Started
Easily ingest Amazon Route 53 log data into the Falcon platform
- Unify threat visibility in a single console
- Simplify data ingestion
- Improve threat hunting
Not A CrowdStrike Customer?
Try CrowdStrikeDetails
Built by
Amazon Web ServicesCategories
Next-Gen SIEM & SOARRequirements
Falcon Next-Gen SIEMSupport


