U.S. Government Disrupts FAMOUS CHOLLIMA Operation with CrowdStrike Assistance Read blog


Your Cart
Added to Cart

There's nothing in your cart
per endpoint / per year
per endpoint / per month

×
![]()
Accelerate operations and boost threat detection
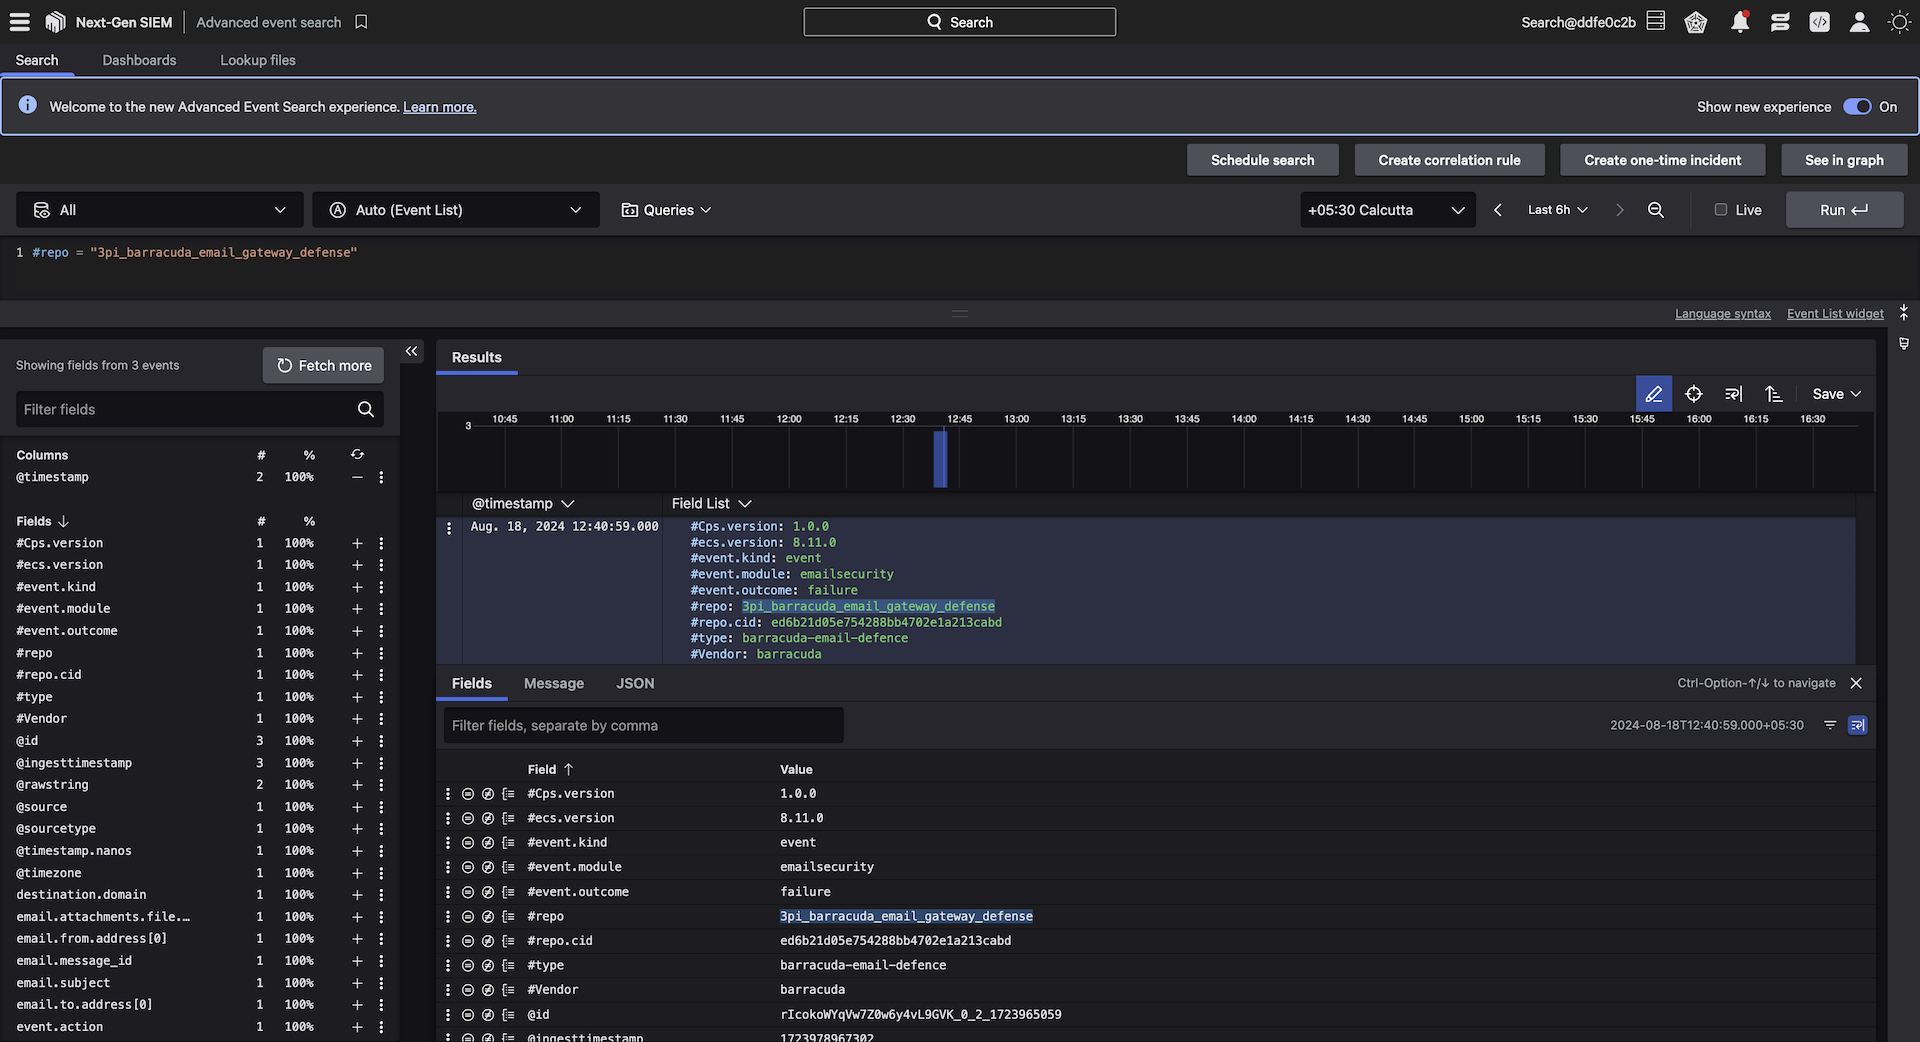
Gain unified visibility and secure your environment by easily ingesting email events, login events and security events from Barracuda Email Security Gateway into the CrowdStrike Falcon® platform. By centralizing email security insights from Barracuda logs and correlating them with other security data within CrowdStrike Falcon Next-Gen SIEM, your team gains enhanced threat detection, streamlined incident response, and an optimized security posture to protect against evolving cyber threats.
- Boost threat detection
Get a unified view of potential threats across your environment by analyzing security logs and events collected from Barracuda Email Security Gateway alongside other security data within the Falcon platform. - Accelerate investigations and incident response
Speed up response with timelines of events and details from Barracuda Email Security Gateway, such as misconfigurations and phishing attacks, using built-in search and filtering capabilities from Falcon Next-Gen SIEM. - Enhance threat hunting
Store and correlate security alerts and events collected from Barracuda Email Security Gateway with other data sources to boost threat hunting, leveraging real-time detections and fast search capabilities to rapidly shut down threats.
Get Started
Ingest email events, security logs, and configuration changes from Barracuda Email Security Gateway
- Boost threat detection
- Accelerate investigations and incident response
- Enhance threat hunting
Not A CrowdStrike Customer?
Try CrowdStrikeDetails
Built by
CrowdStrikeCategories
Email Security Next-Gen SIEM & SOARRequirements
Falcon Next-Gen SIEM