U.S. Government Disrupts FAMOUS CHOLLIMA Operation with CrowdStrike Assistance Read blog


Your Cart
Added to Cart

There's nothing in your cart
per endpoint / per year
per endpoint / per month
×
![]()
Accelerate operations and boost threat detection
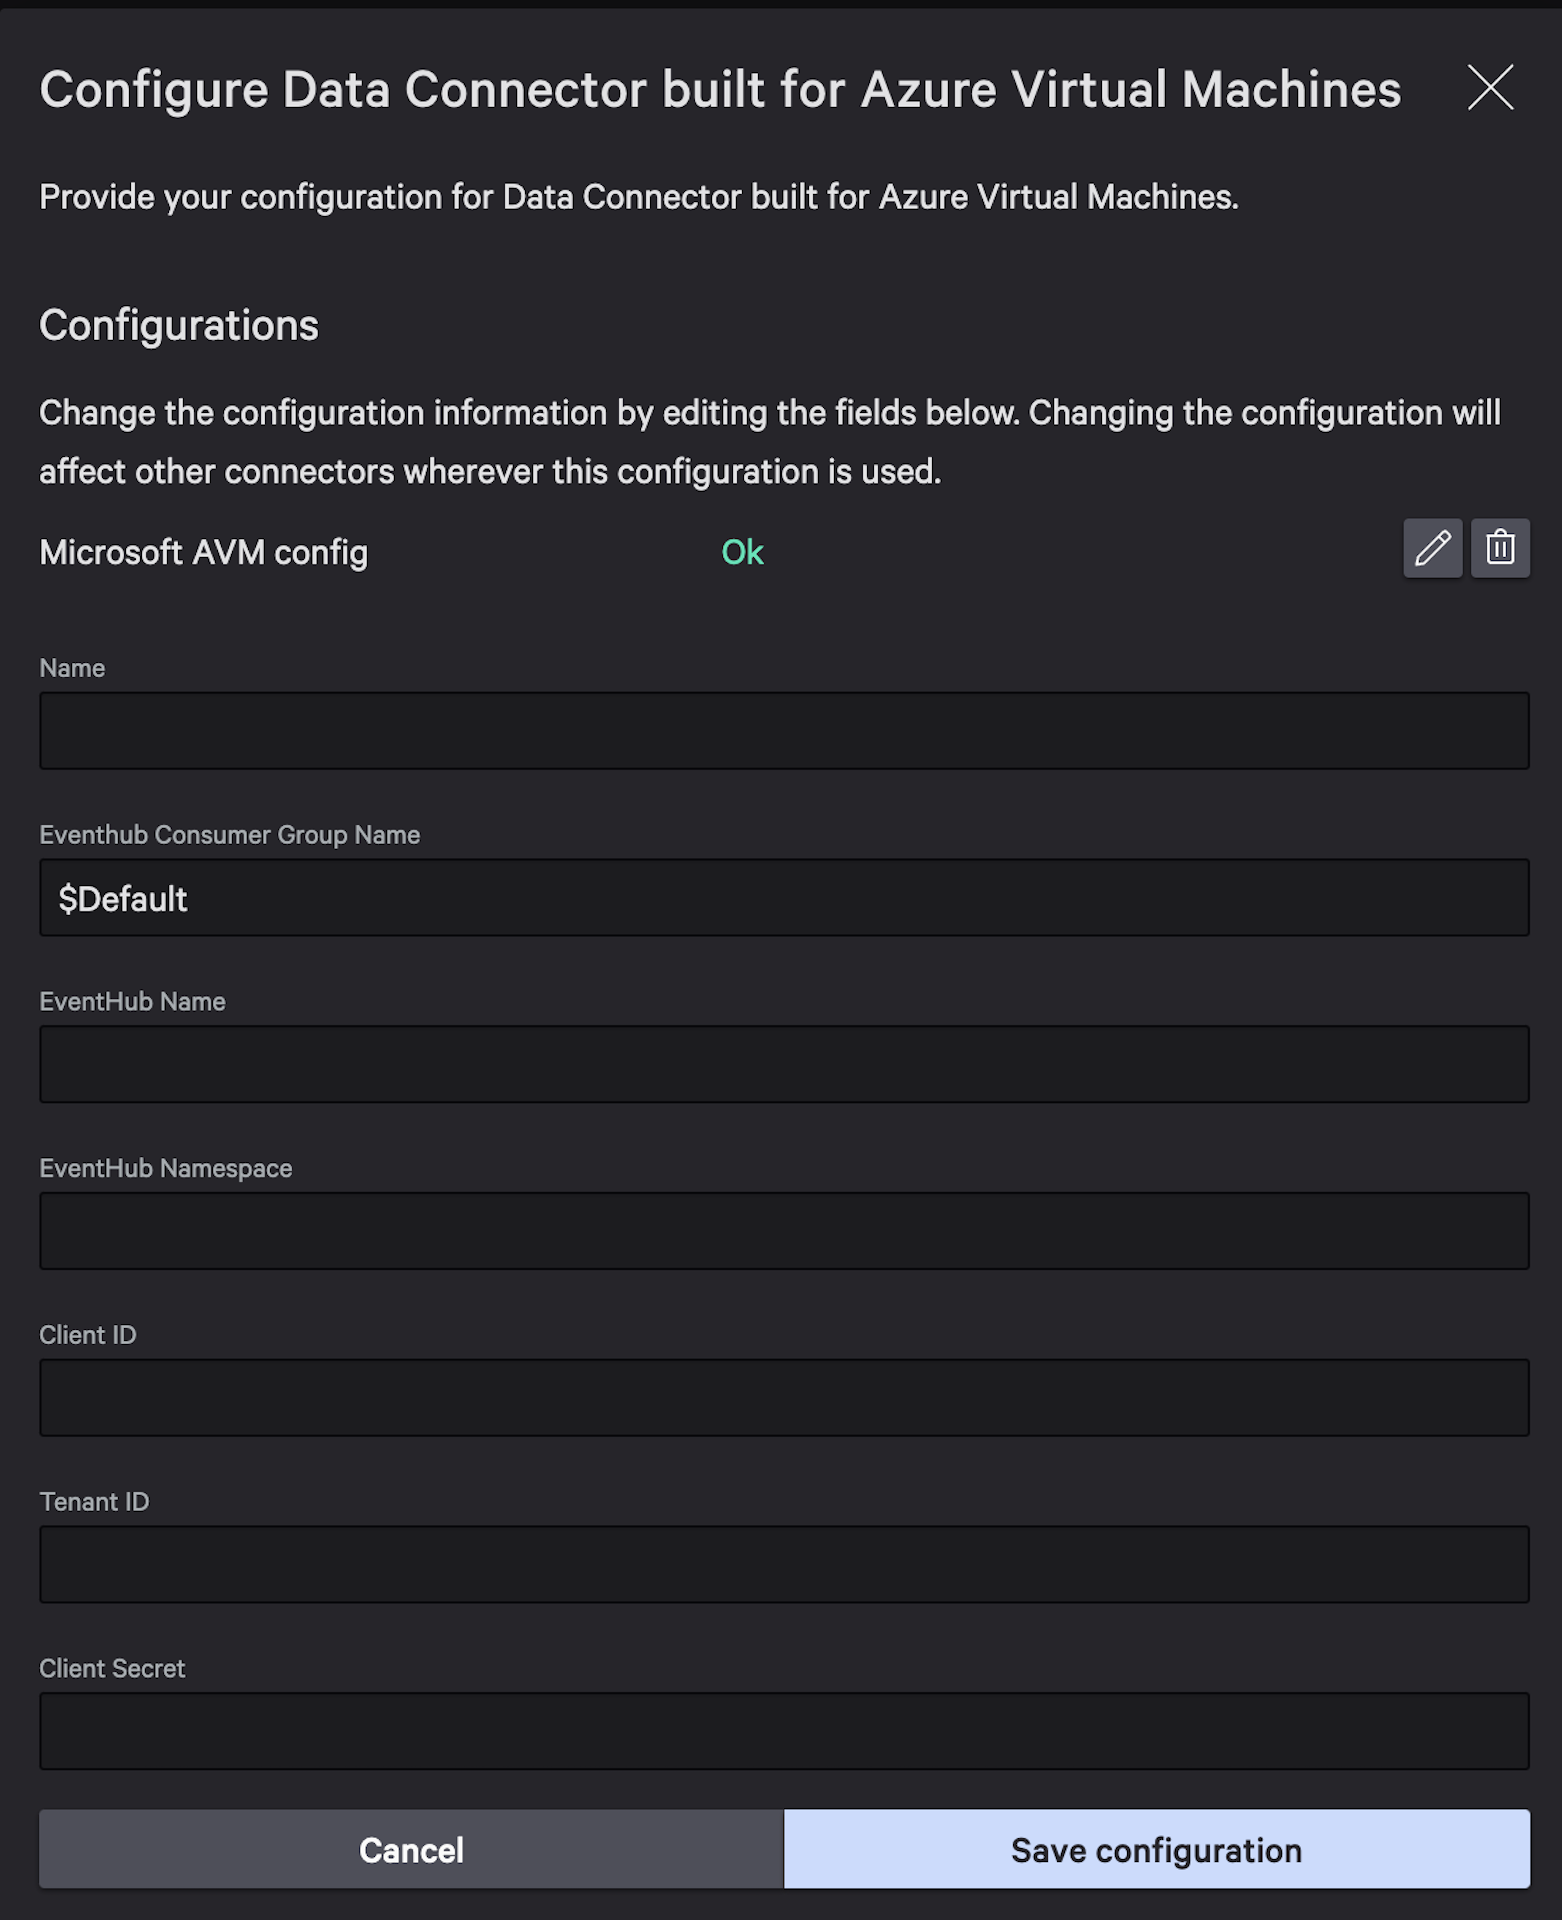
Gain unified visibility of your environment by easily ingesting Windows and Linux events from Azure Virtual Machines into the CrowdStrike Falcon® platform. By centralizing and correlating insights from Azure Virtual Machines, CrowdStrike, and additional third parties within CrowdStrike Falcon® Next-Gen SIEM, your team gains enhanced threat detection, streamlined incident response, and an optimized security posture to ultimately protect against evolving cyber threats
- Streamline investigations and incident response
Accelerate response for threats with detailed timelines of events and actionable forensic data from Azure Virtual Machine events using built-in search and filtering capabilities from Falcon Next-Gen SIEM - Improve threat hunting
Store and correlate Azure Virtual Machine data with other data sources to boost threat hunting, leveraging real-time detections and blazing-fast search to rapidly shut down threats
Get Started
Ingest Windows and Linux events from Azure Virtual Machines for further threat detection and investigation
- Streamline investigations and incident response
- Improve threat hunting
Not A CrowdStrike Customer?
Try CrowdStrike