CrowdStrike Protects Customers from Threats Delivered via PHP2Shell Read blog


Your Cart
Added to Cart

There's nothing in your cart
per endpoint / per year
per endpoint / per month
×
![]()
Accelerate operations and boost threat detection
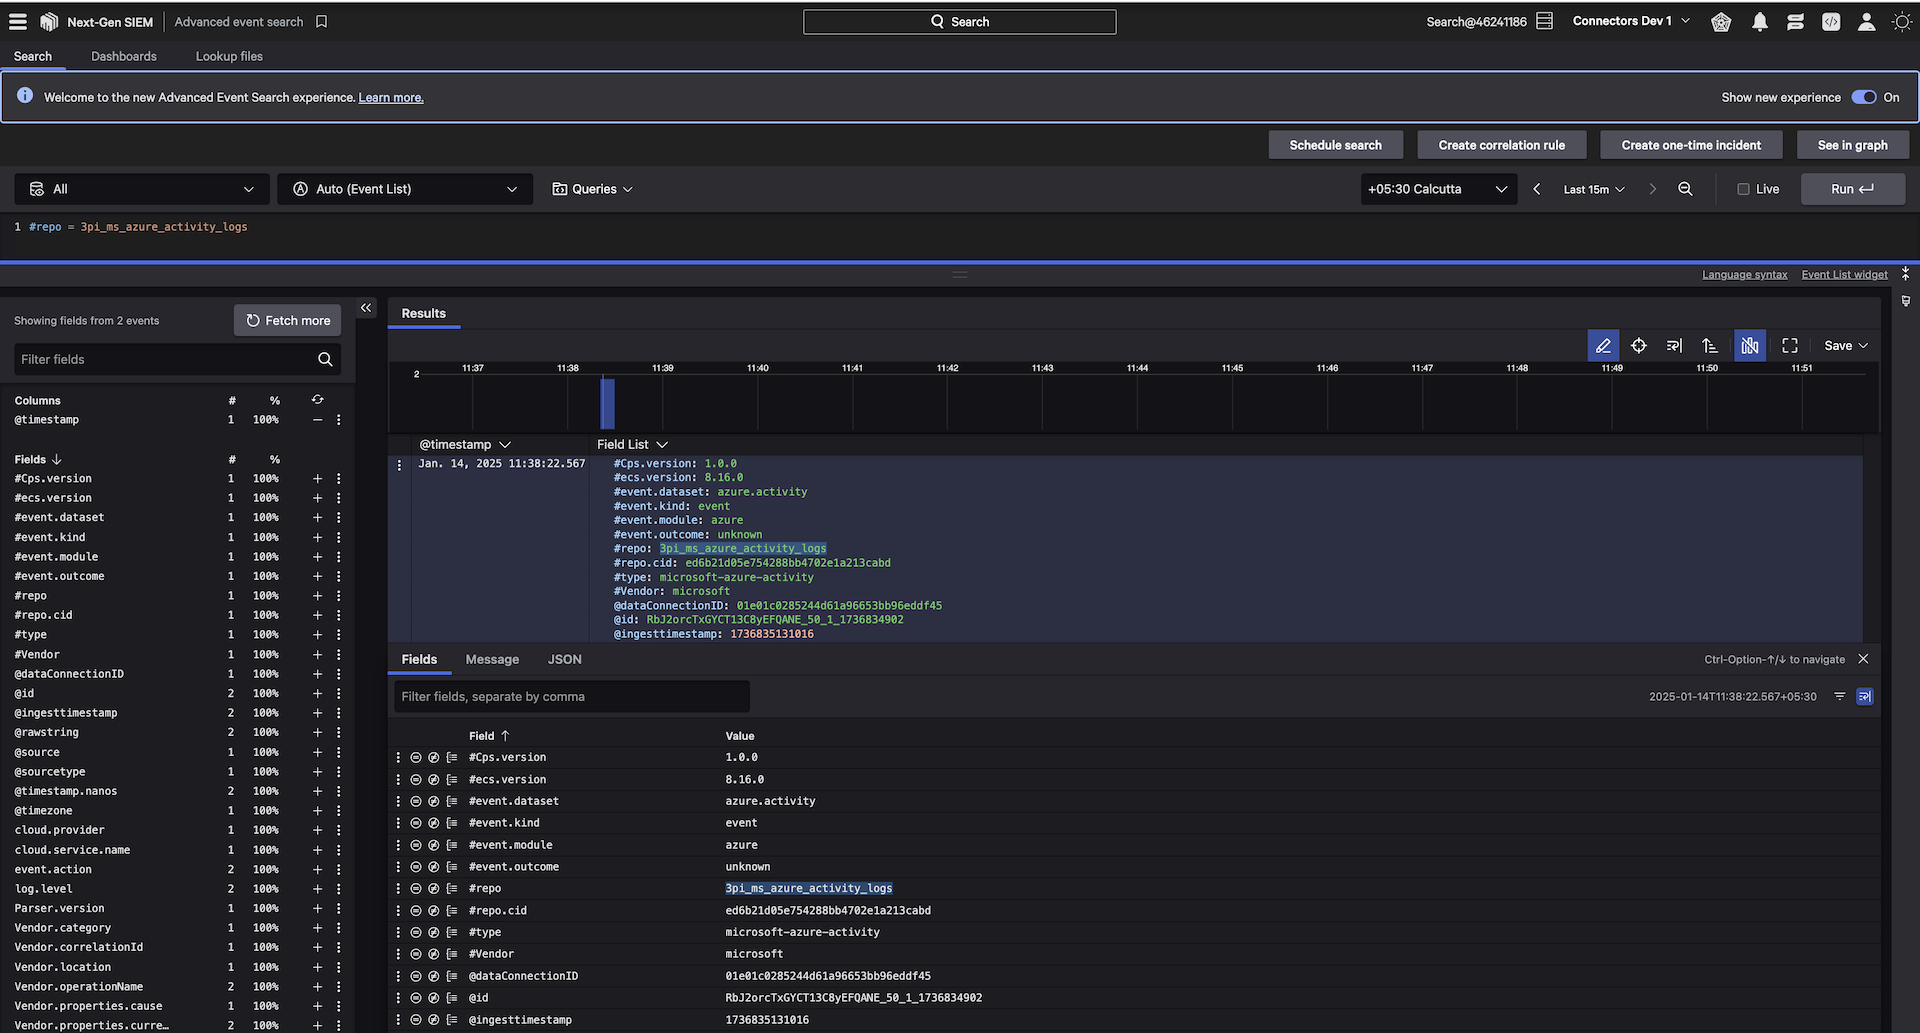
Gain unified visibility of your cloud environment by easily ingesting Microsoft Azure activity logs into the CrowdStrike Falcon® platform. By centralizing and correlating insights from your Azure resources, CrowdStrike, and additional third parties within CrowdStrike Falcon® Next-Gen SIEM, your team gains enhanced threat detection, streamlined incident response, and an optimized security posture across your hybrid cloud environment to ultimately protect against evolving cyber threats.
- Boost cloud threat detection
Get a unified view of potential threats within your cloud environment by analyzing activity logs collected from Azure resources alongside other security telemetry within the Falcon platform - Accelerate investigations and incident response
Speed up response with timelines of events and actionable forensic data from Azure resources, such as unauthorized access and configuration changes, using built-in search and filtering capabilities from Falcon Next-Gen SIEM - Enhance threat hunting
Store and correlate Microsoft Azure Activity log data with other data sources to boost threat hunting, leveraging real-time detections and blazing-fast search to rapidly shut down threats
Get Started
Easily ingest Microsoft Azure activity logs for further analysis, threat detection and investigation
- Boost cloud threat detection
- Accelerate investigations and incident response
- Enhance threat hunting
Not A CrowdStrike Customer?
Try CrowdStrike