U.S. Government Disrupts FAMOUS CHOLLIMA Operation with CrowdStrike Assistance Read blog


Your Cart
Added to Cart

There's nothing in your cart
per endpoint / per year
per endpoint / per month
×
![]()
Accelerate operations and boost threat detection
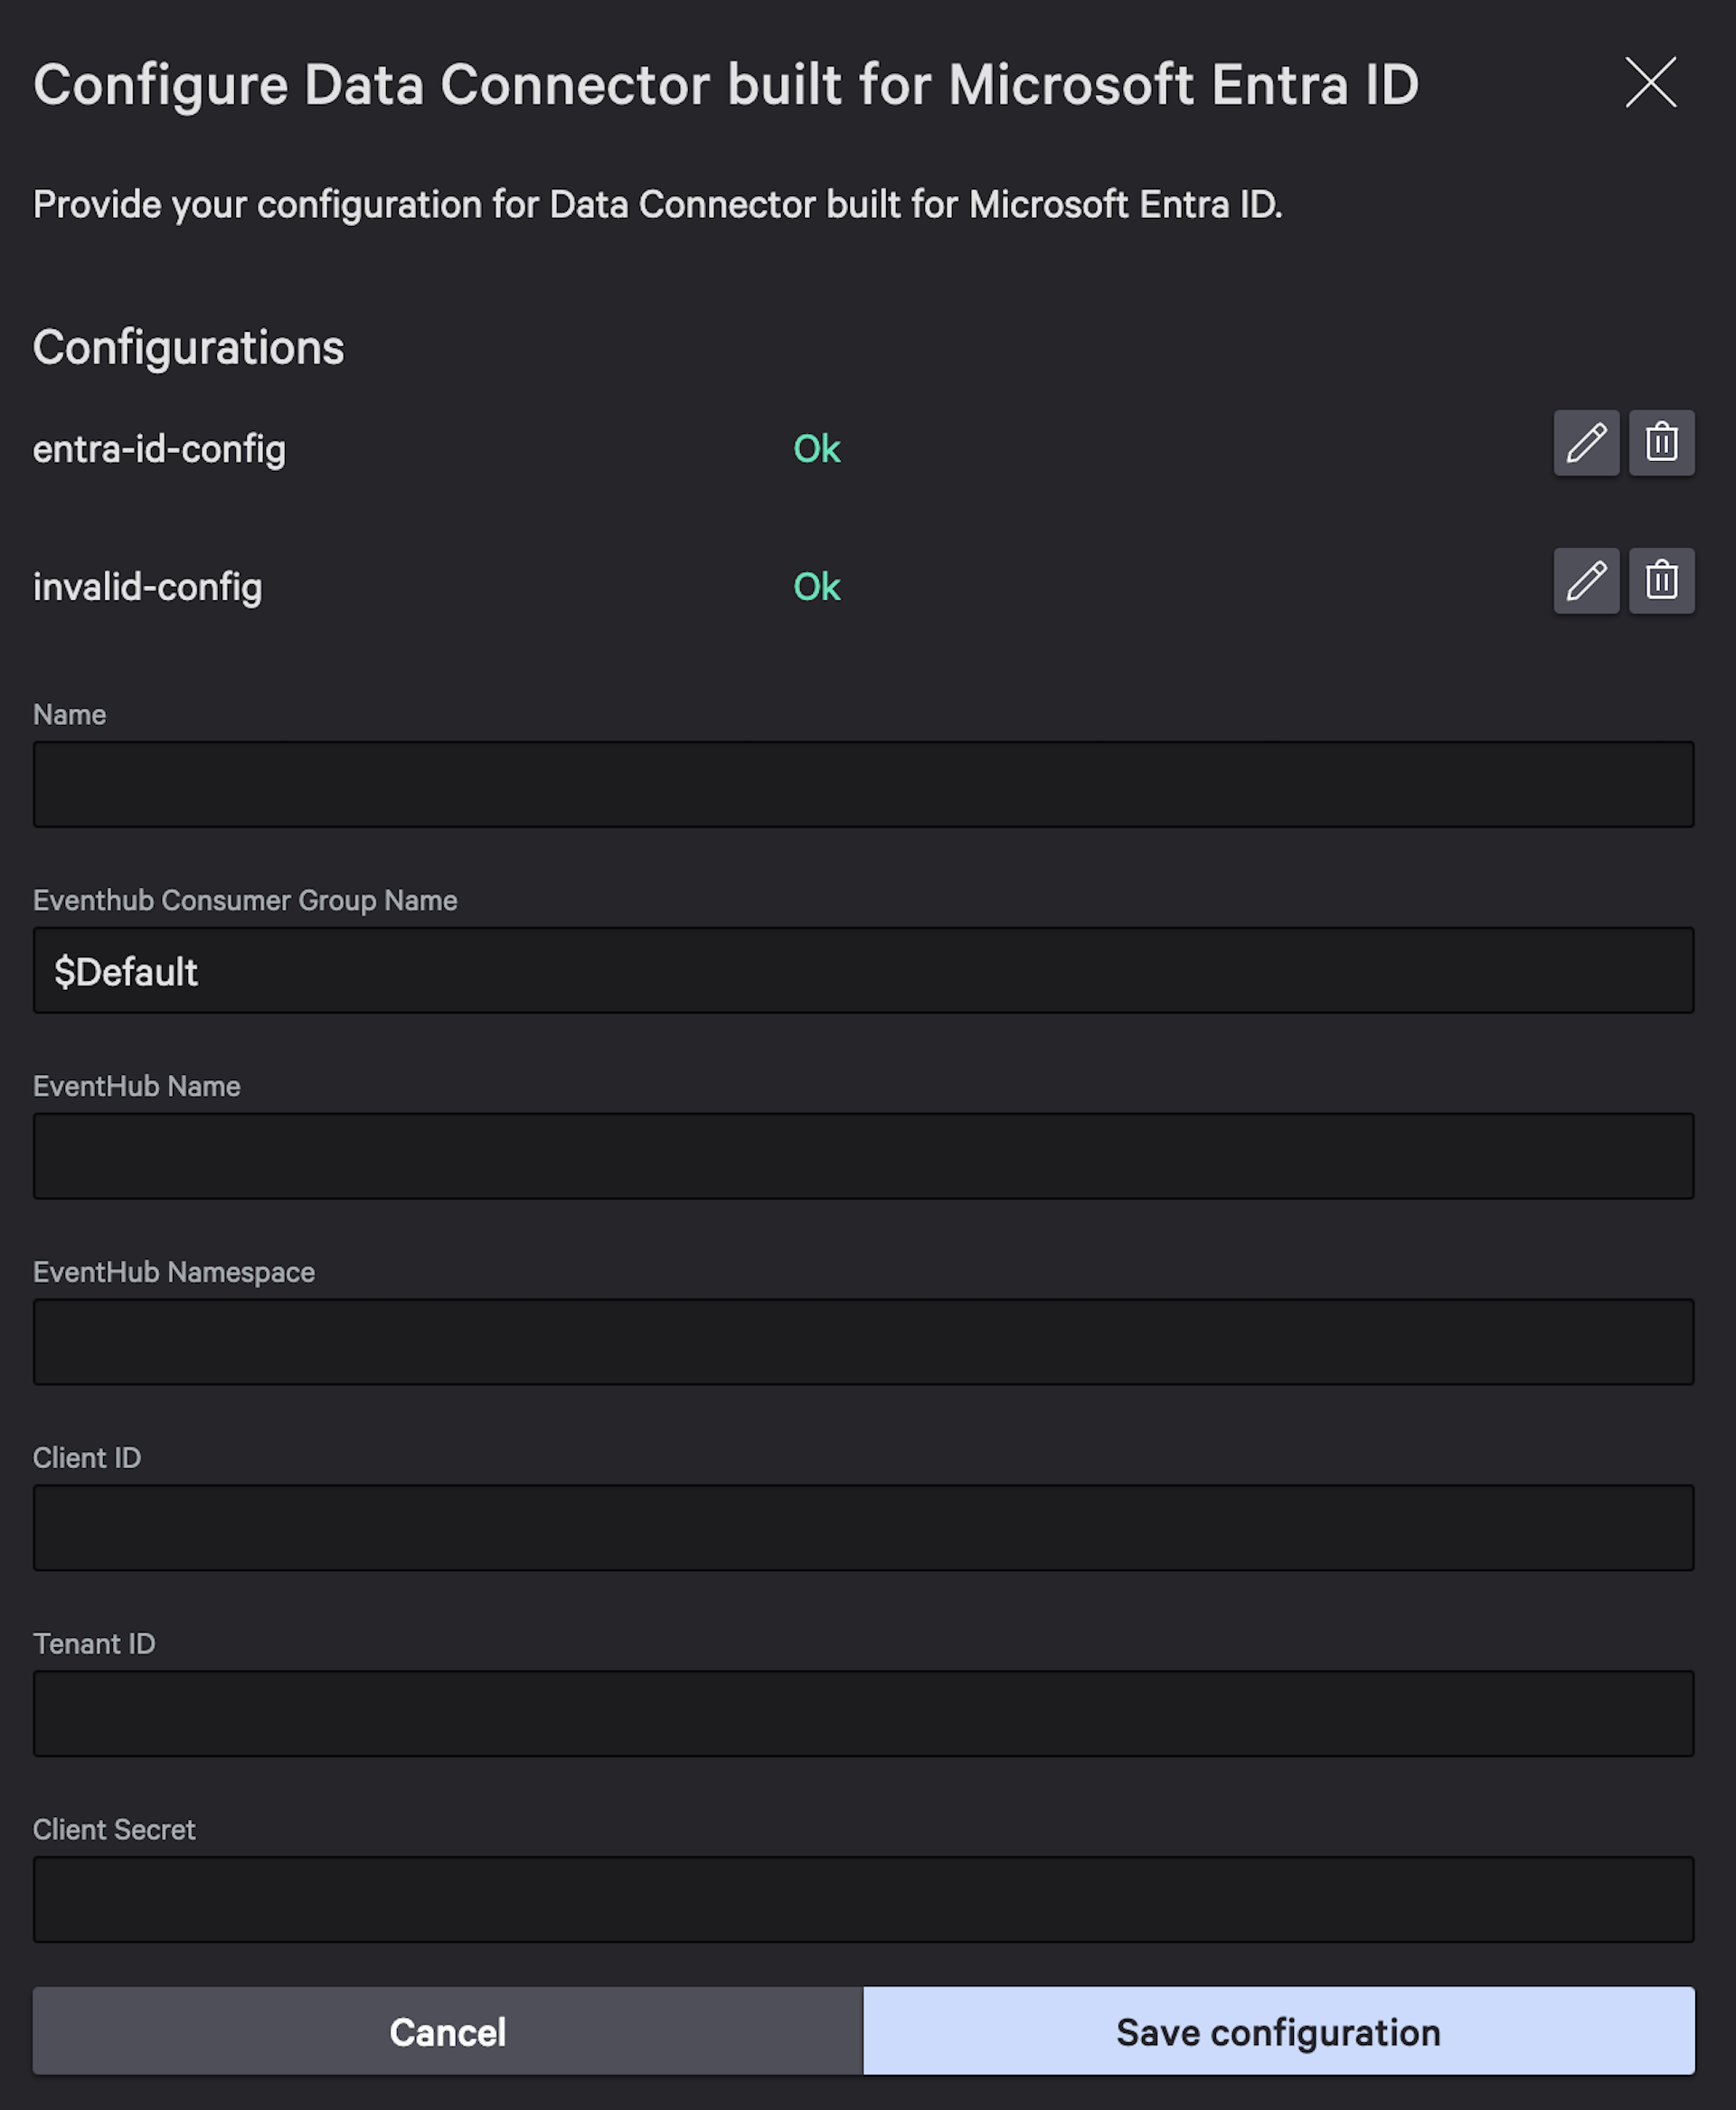
Gain unified visibility of your environment and identity security data by easily ingesting Microsoft Entra ID activity logs into the CrowdStrike Falcon® platform. By centralizing and correlating cloud identity and access management insights from Microsoft Entra ID, CrowdStrike, and additional third parties within CrowdStrike Falcon® Next-Gen SIEM, your team gains enhanced threat detection, streamlined incident response, and an optimized security posture to ultimately protect against evolving cyber threats
- Enhance cloud identity and access management
Gain a comprehensive view of potential cloud identity threats by analyzing Microsoft Entra ID activity logs with other security telemetry within the Falcon platform - Streamline investigations and incident response
Accelerate response of identity based threats with detailed timelines of events and actionable forensic data from Microsoft Entra ID, such as unauthorized access, phishing and ransomware attacks, using built-in search and filtering capabilities from Falcon Next-Gen SIEM - Improve threat hunting
Store and correlate Microsoft Entra ID activity data with other data sources to boost threat hunting, leveraging real-time detections and blazing-fast search to rapidly shut down threats
Get Started
Ingest Microsoft Exchange Entra ID data for further analysis, threat detection and investigation
- Enhance cloud identity and access management
- Streamline investigations and incident response
- Improve threat hunting
Not A CrowdStrike Customer?
Try CrowdStrikeDetails
Built by
CrowdStrikeCategories
Identity Security Next-Gen SIEM & SOARRequirements
Falcon Next-Gen SIEM