U.S. Government Disrupts FAMOUS CHOLLIMA Operation with CrowdStrike Assistance Read blog


Your Cart
Added to Cart

There's nothing in your cart
per endpoint / per year
per endpoint / per month

×
![]()
Get critical visibility of your attack surface
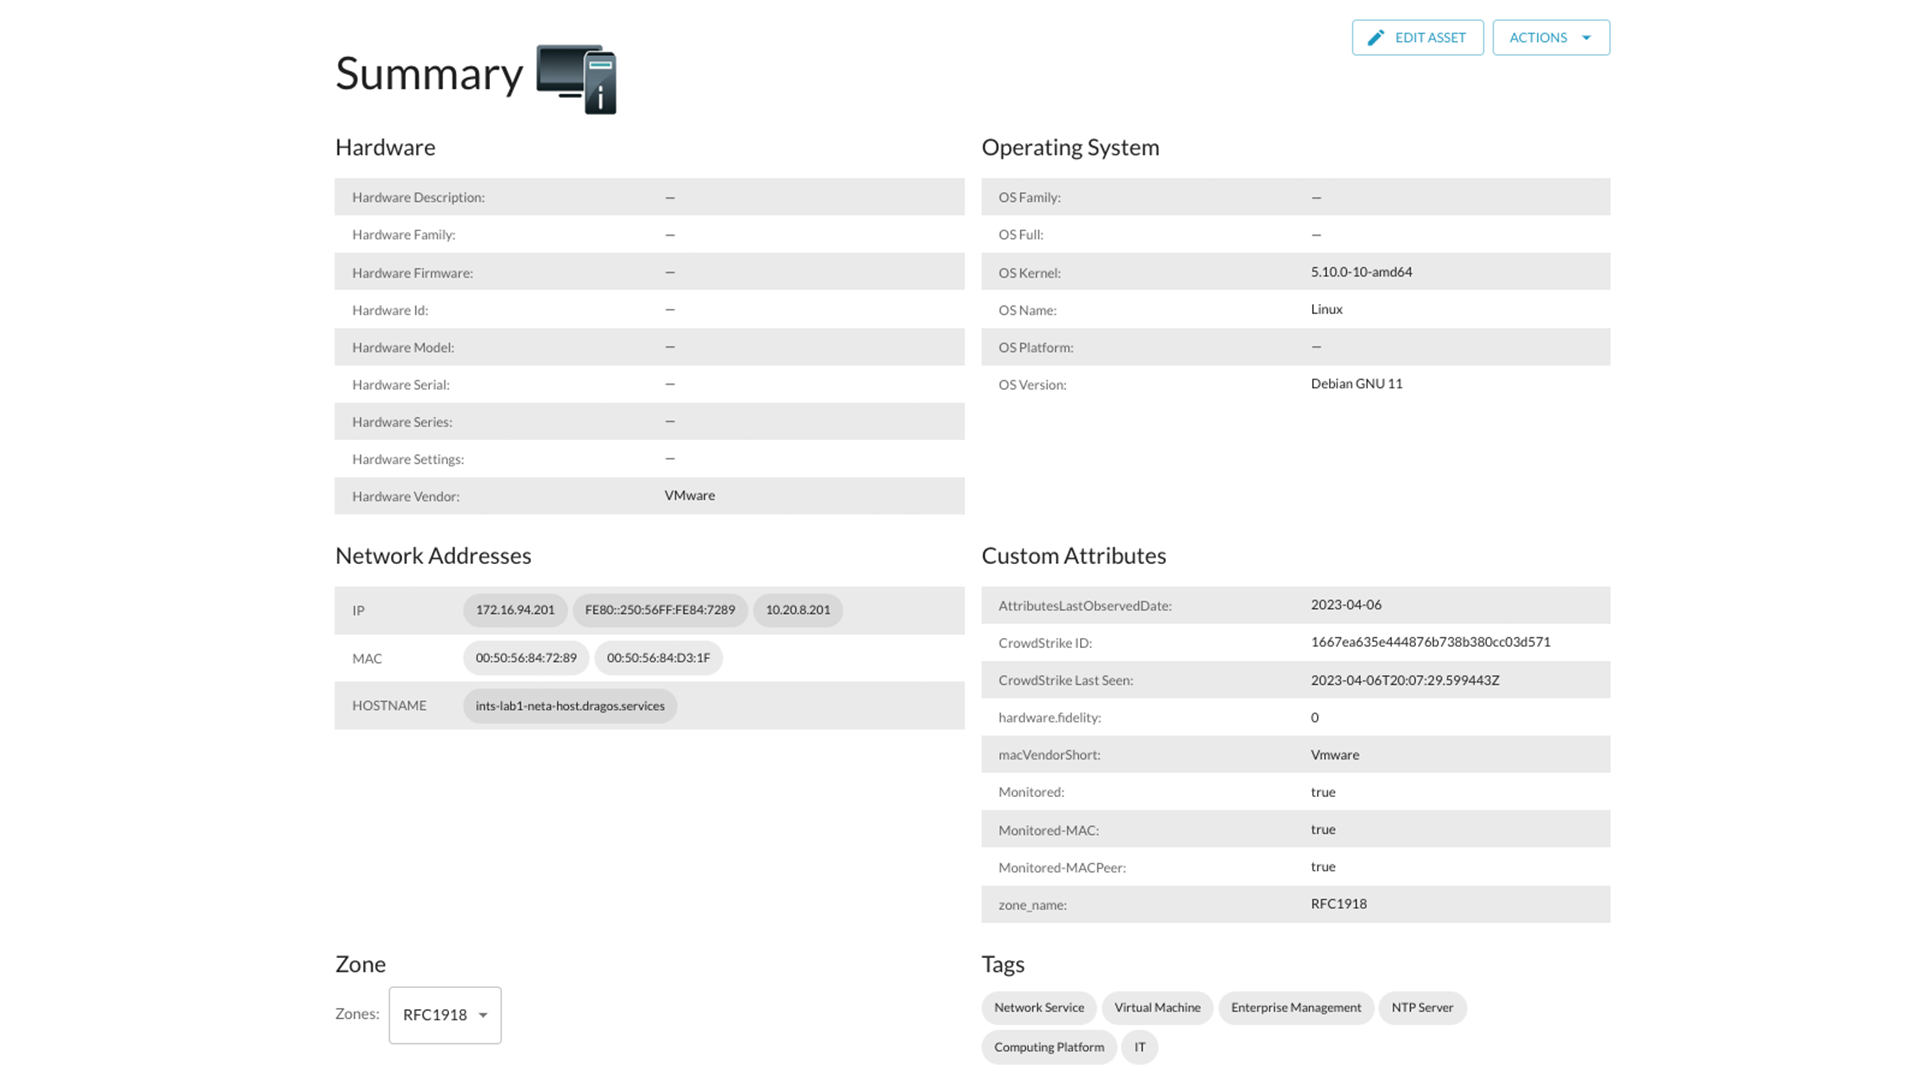
Dragos integrates with CrowdStrike to provide you with enhanced operational technology (OT) asset visibility and threat detection by enriching asset information with CrowdStrike security data. Dragos pulls endpoint detection and response (EDR) asset details and security data from the CrowdStrike Falcon® platform to enrich and enhance device information of known assets in the Dragos Platform, including IP address, MAC (Media Access Control) address, endpoint hostname, associated active directory (AD) Domain, operating system (OS) data fields and additional custom attributes to provide you with critical visibility of your attack surface. The integration also provides additional context on edge devices in OT environments, allowing users to forward Falcon detections on known assets to the Dragos Platform to speed up elusive threat detection and response.
- Improved asset visibility and threat detection
Enable combined, comprehensive, and continuous visibility into threats on your OT networks by leveraging the device details and detections from CrowdStrike that could impact edge ICS devices. - Coordinated response for malicious activity
Coordinate response efforts across response teams for known OT assets, including edge ICS devices, based on detections in the Dragos Platform that leverage CrowdStrike Indicators of Compromise (IOCs).
Get Started
Improve OT asset visibility and threat detection
- Improved asset visibility and threat detection
- Coordinated response for malicious activity
Not A CrowdStrike Customer?
Try CrowdStrikeDocuments


