Discover the latest news and innovations from Fal.Con Europe Learn more


Your Cart
Added to Cart

There's nothing in your cart
per endpoint / per year
per endpoint / per month

×
![]()
Accelerate operations and boost threat detection
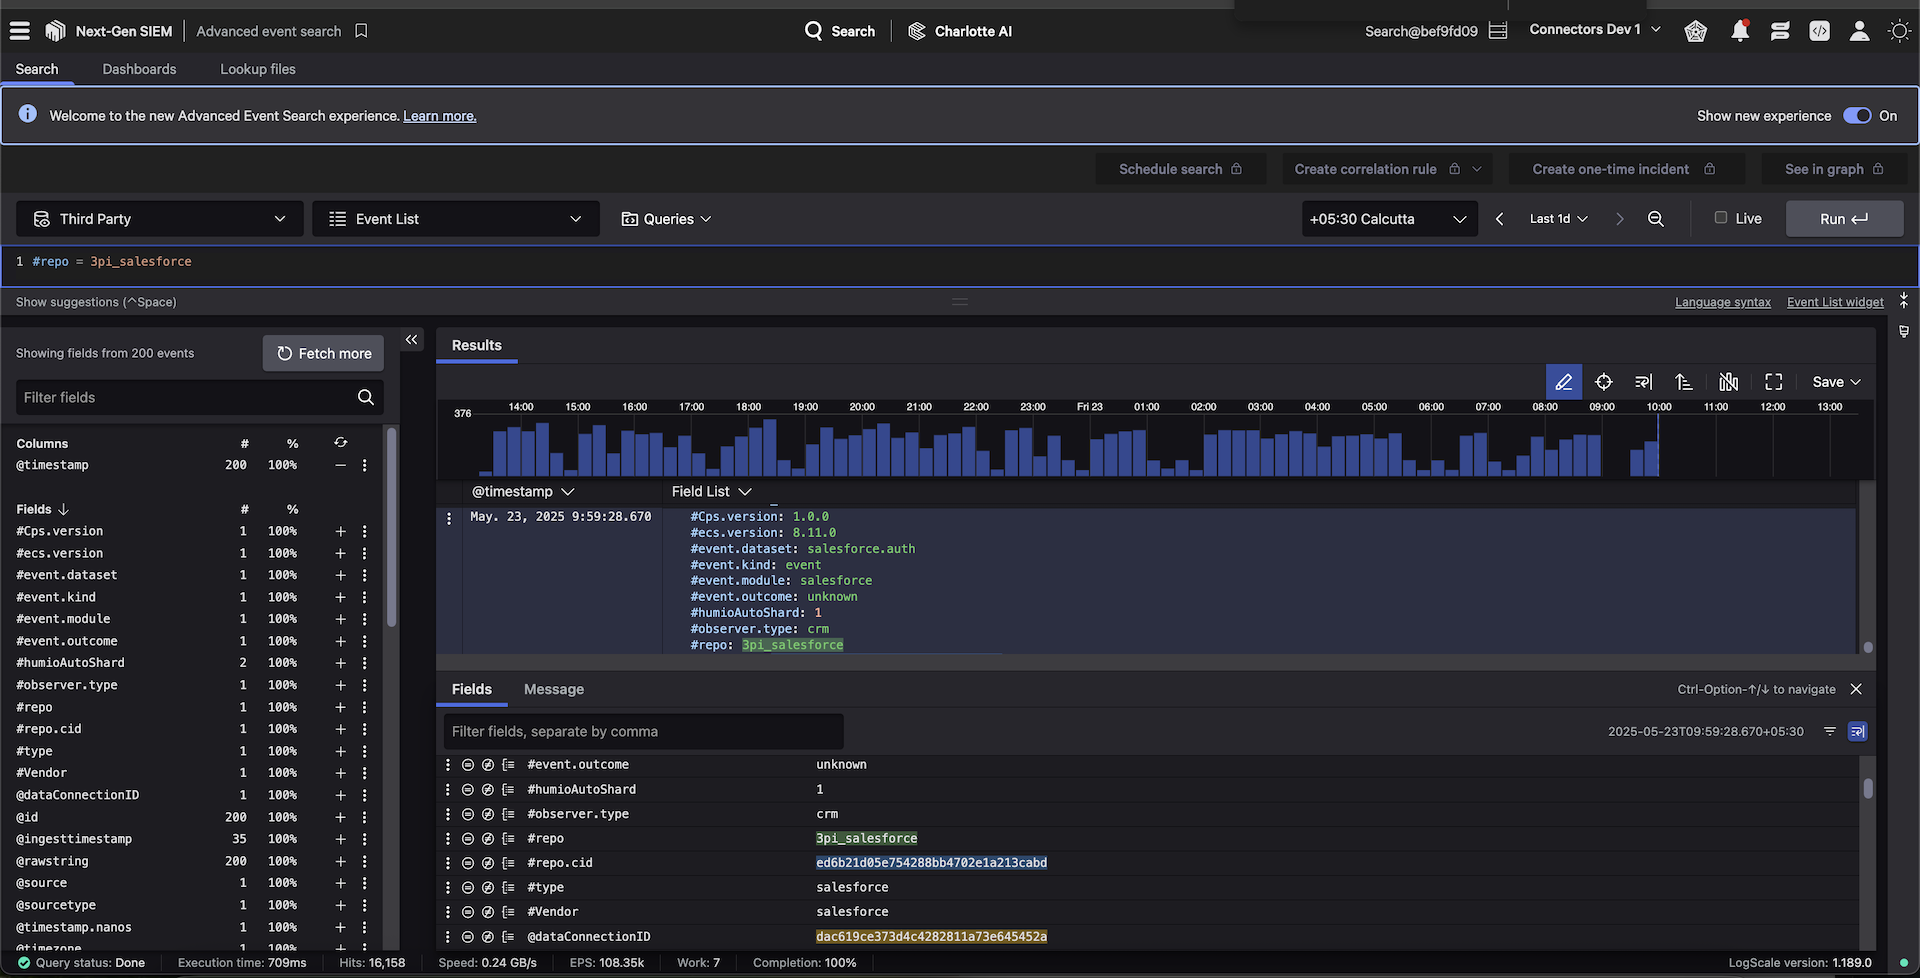
Gain unified visibility of your Salesforce authentication activities by easily ingesting Salesforce login audit logs into the CrowdStrike Falcon® platform. By centralizing and correlating audit logs from Salesforce, CrowdStrike, and additional third parties within CrowdStrike Falcon® Next-Gen SIEM, your team gains enhanced threat detection, streamlined incident response, and an optimized security posture to ultimately protect against unauthorized access and authentication-based threats.
- Boost identity threat detection
Get a unified view of potential authentication threats by analyzing login audit logs collected from Salesforce, alongside other security telemetry within the Falcon platform - Accelerate investigations and incident response
Speed up response with timelines of login events from Salesforce, such as suspicious login patterns, unauthorized LoginAs attempts, and abnormal URI access, using built-in search and filtering capabilities from Falcon Next-Gen SIEM - Enhance threat hunting
Store and correlate Salesforce login audit logs with other data sources to boost threat hunting, leveraging real-time detections and blazing-fast search to rapidly identify and respond to authentication-based threats
Get Started
Ingest Salesforce audit logs into the Falcon platform
- Boost identity threat detection
- Accelerate investigations and incident response
- Enhance threat hunting
Not A CrowdStrike Customer?
Try CrowdStrike


