Discover the latest news and innovations from Fal.Con Europe Learn more


Your Cart
Added to Cart

There's nothing in your cart
per endpoint / per year
per endpoint / per month

×
![]()
Accelerate operations and boost threat detection
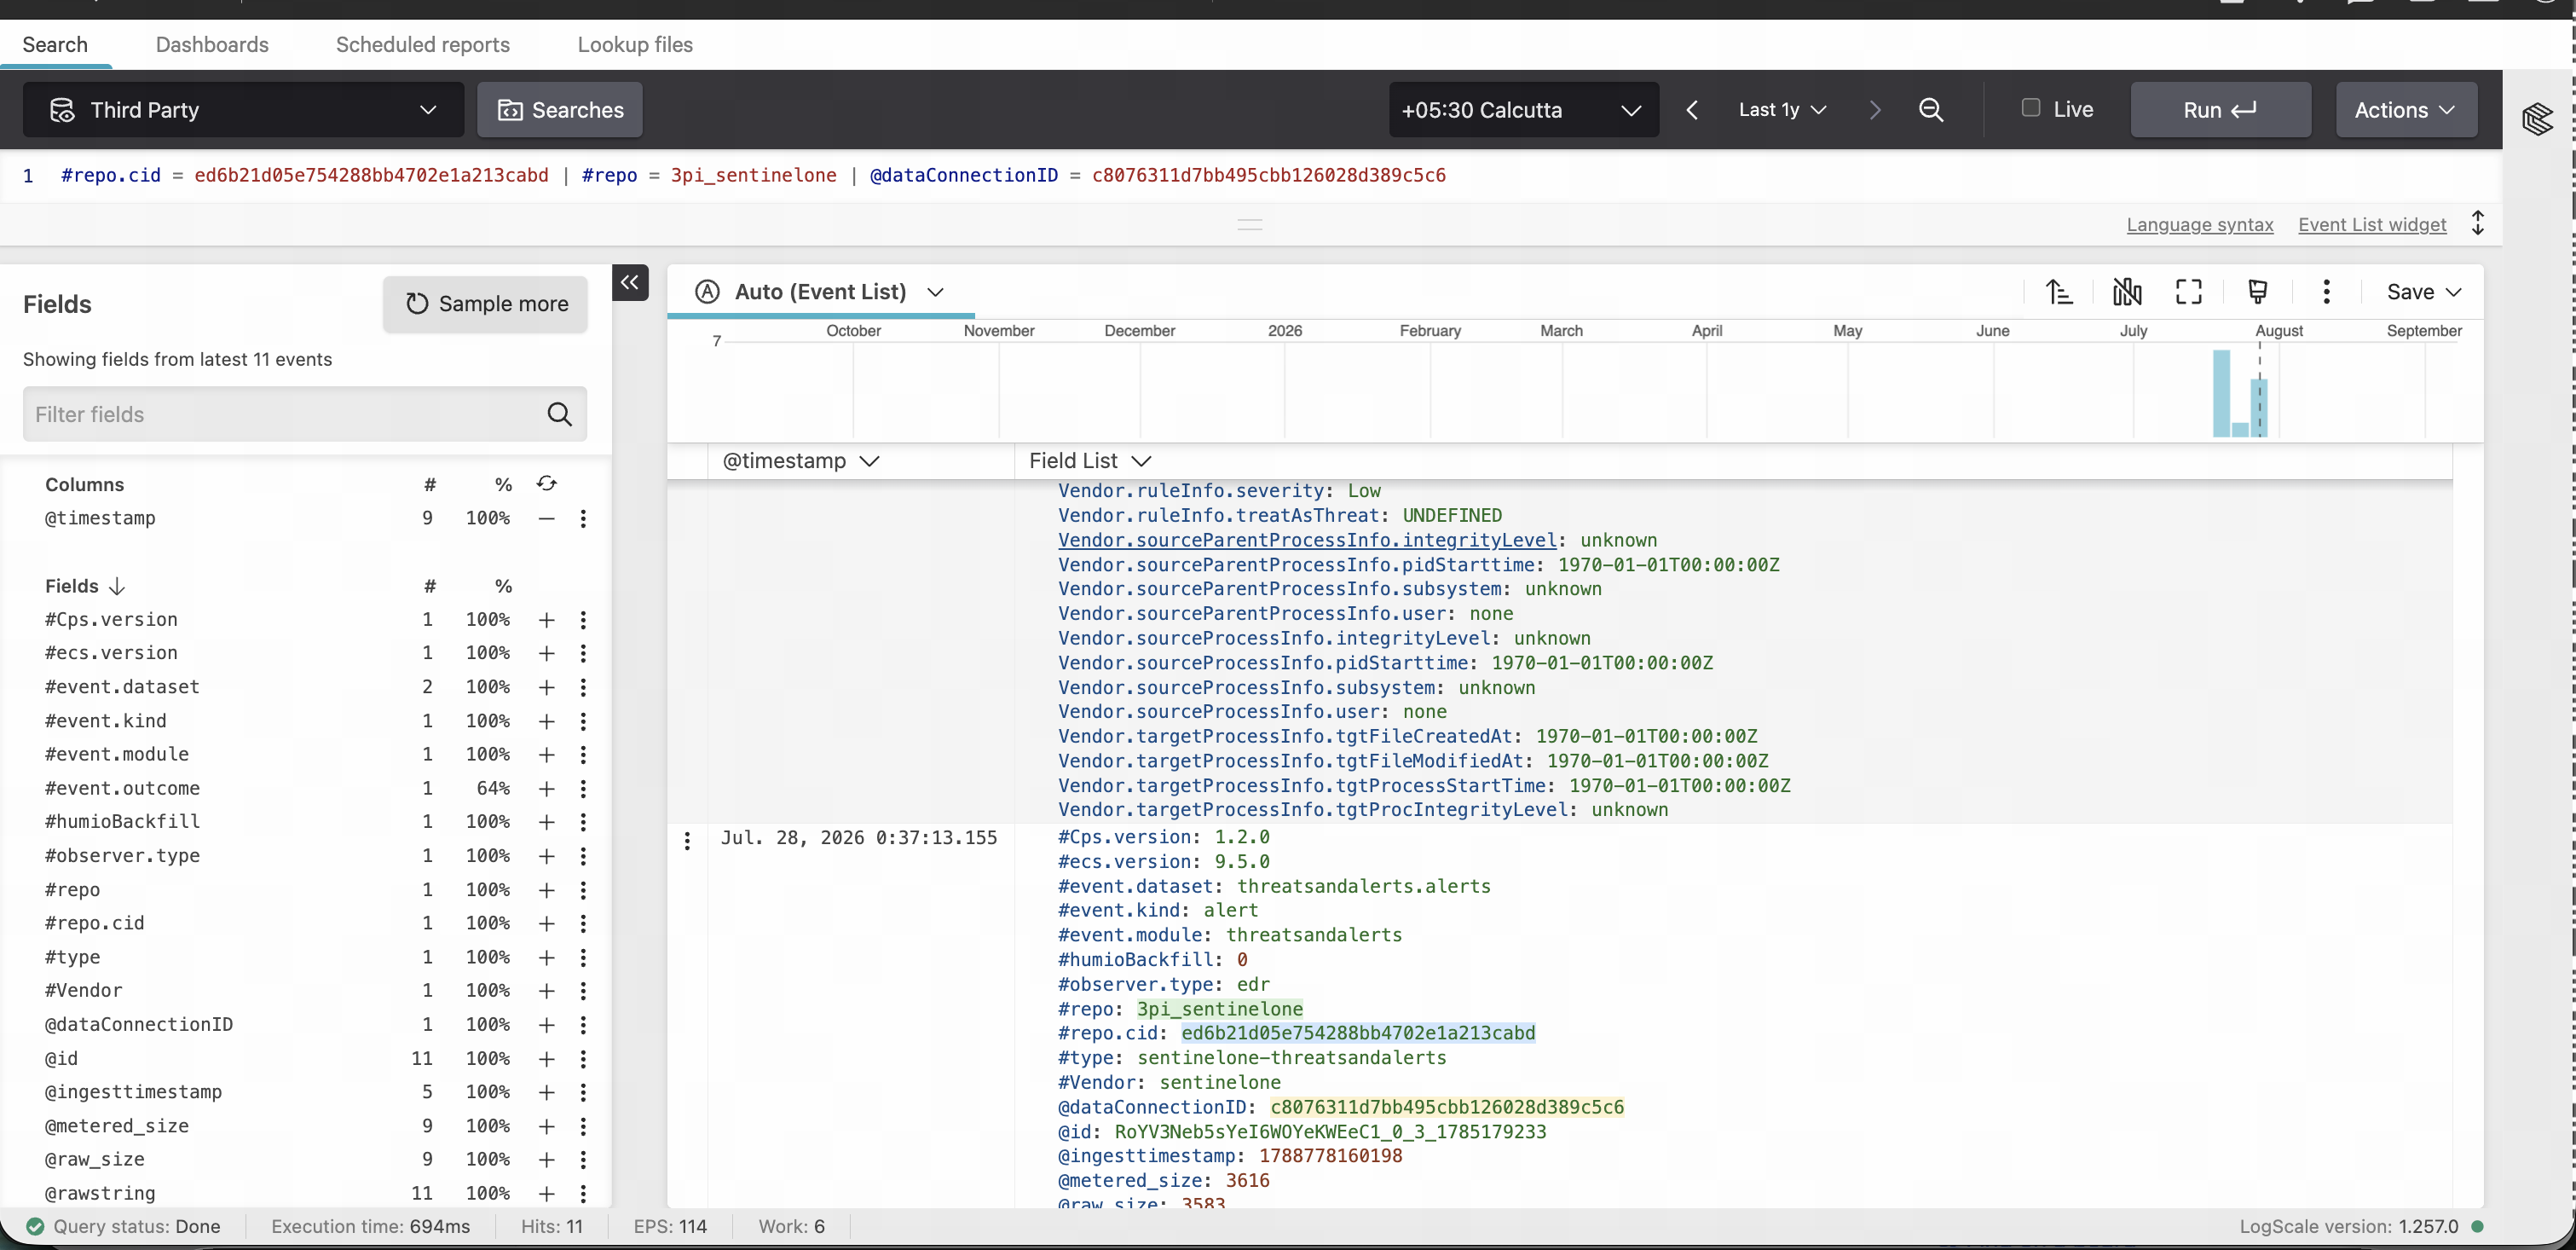
The SentinelOne Threats and Alerts connector ingests threat and alert events from SentinelOne into CrowdStrike Falcon, providing continuous visibility into endpoint threats and cloud-based detections across your organization. Threat incidents, STAR rule alerts, severity classifications, and analyst verdicts are all collected via SentinelOne's Management API and delivered to Falcon Next-Gen SIEM — giving security teams a consolidated view of SentinelOne detections alongside CrowdStrike endpoint, identity, and network telemetry for faster investigation and response.
- Unified threat visibility
Ingest all SentinelOne threat incidents and cloud detection alerts — including severity, analyst verdicts, incident status, and STAR rule matches — into a single timeline in Falcon Next-Gen SIEM. - Cross-platform threat correlation
Correlate SentinelOne endpoint detections and cloud alerts with CrowdStrike telemetry to identify multi-vector attacks, lateral movement, and gaps in coverage across security tools. - Continuous, gap-free data collection
Automatically ingest new threats and alerts on a recurring schedule with built-in resilience — ensuring complete coverage without manual intervention or missed events.
Get Started
Ingest SentinelOne threats and alerts into Falcon
- Unified threat visibility
- Cross-platform threat correlation
- Continuous, gap-free data collection
Not A CrowdStrike Customer?
Try CrowdStrike


