Discover the latest news and innovations from Fal.Con Europe Learn more


Your Cart
Added to Cart

There's nothing in your cart
per endpoint / per year
per endpoint / per month

×
![]()
Accelerate operations and boost threat detection
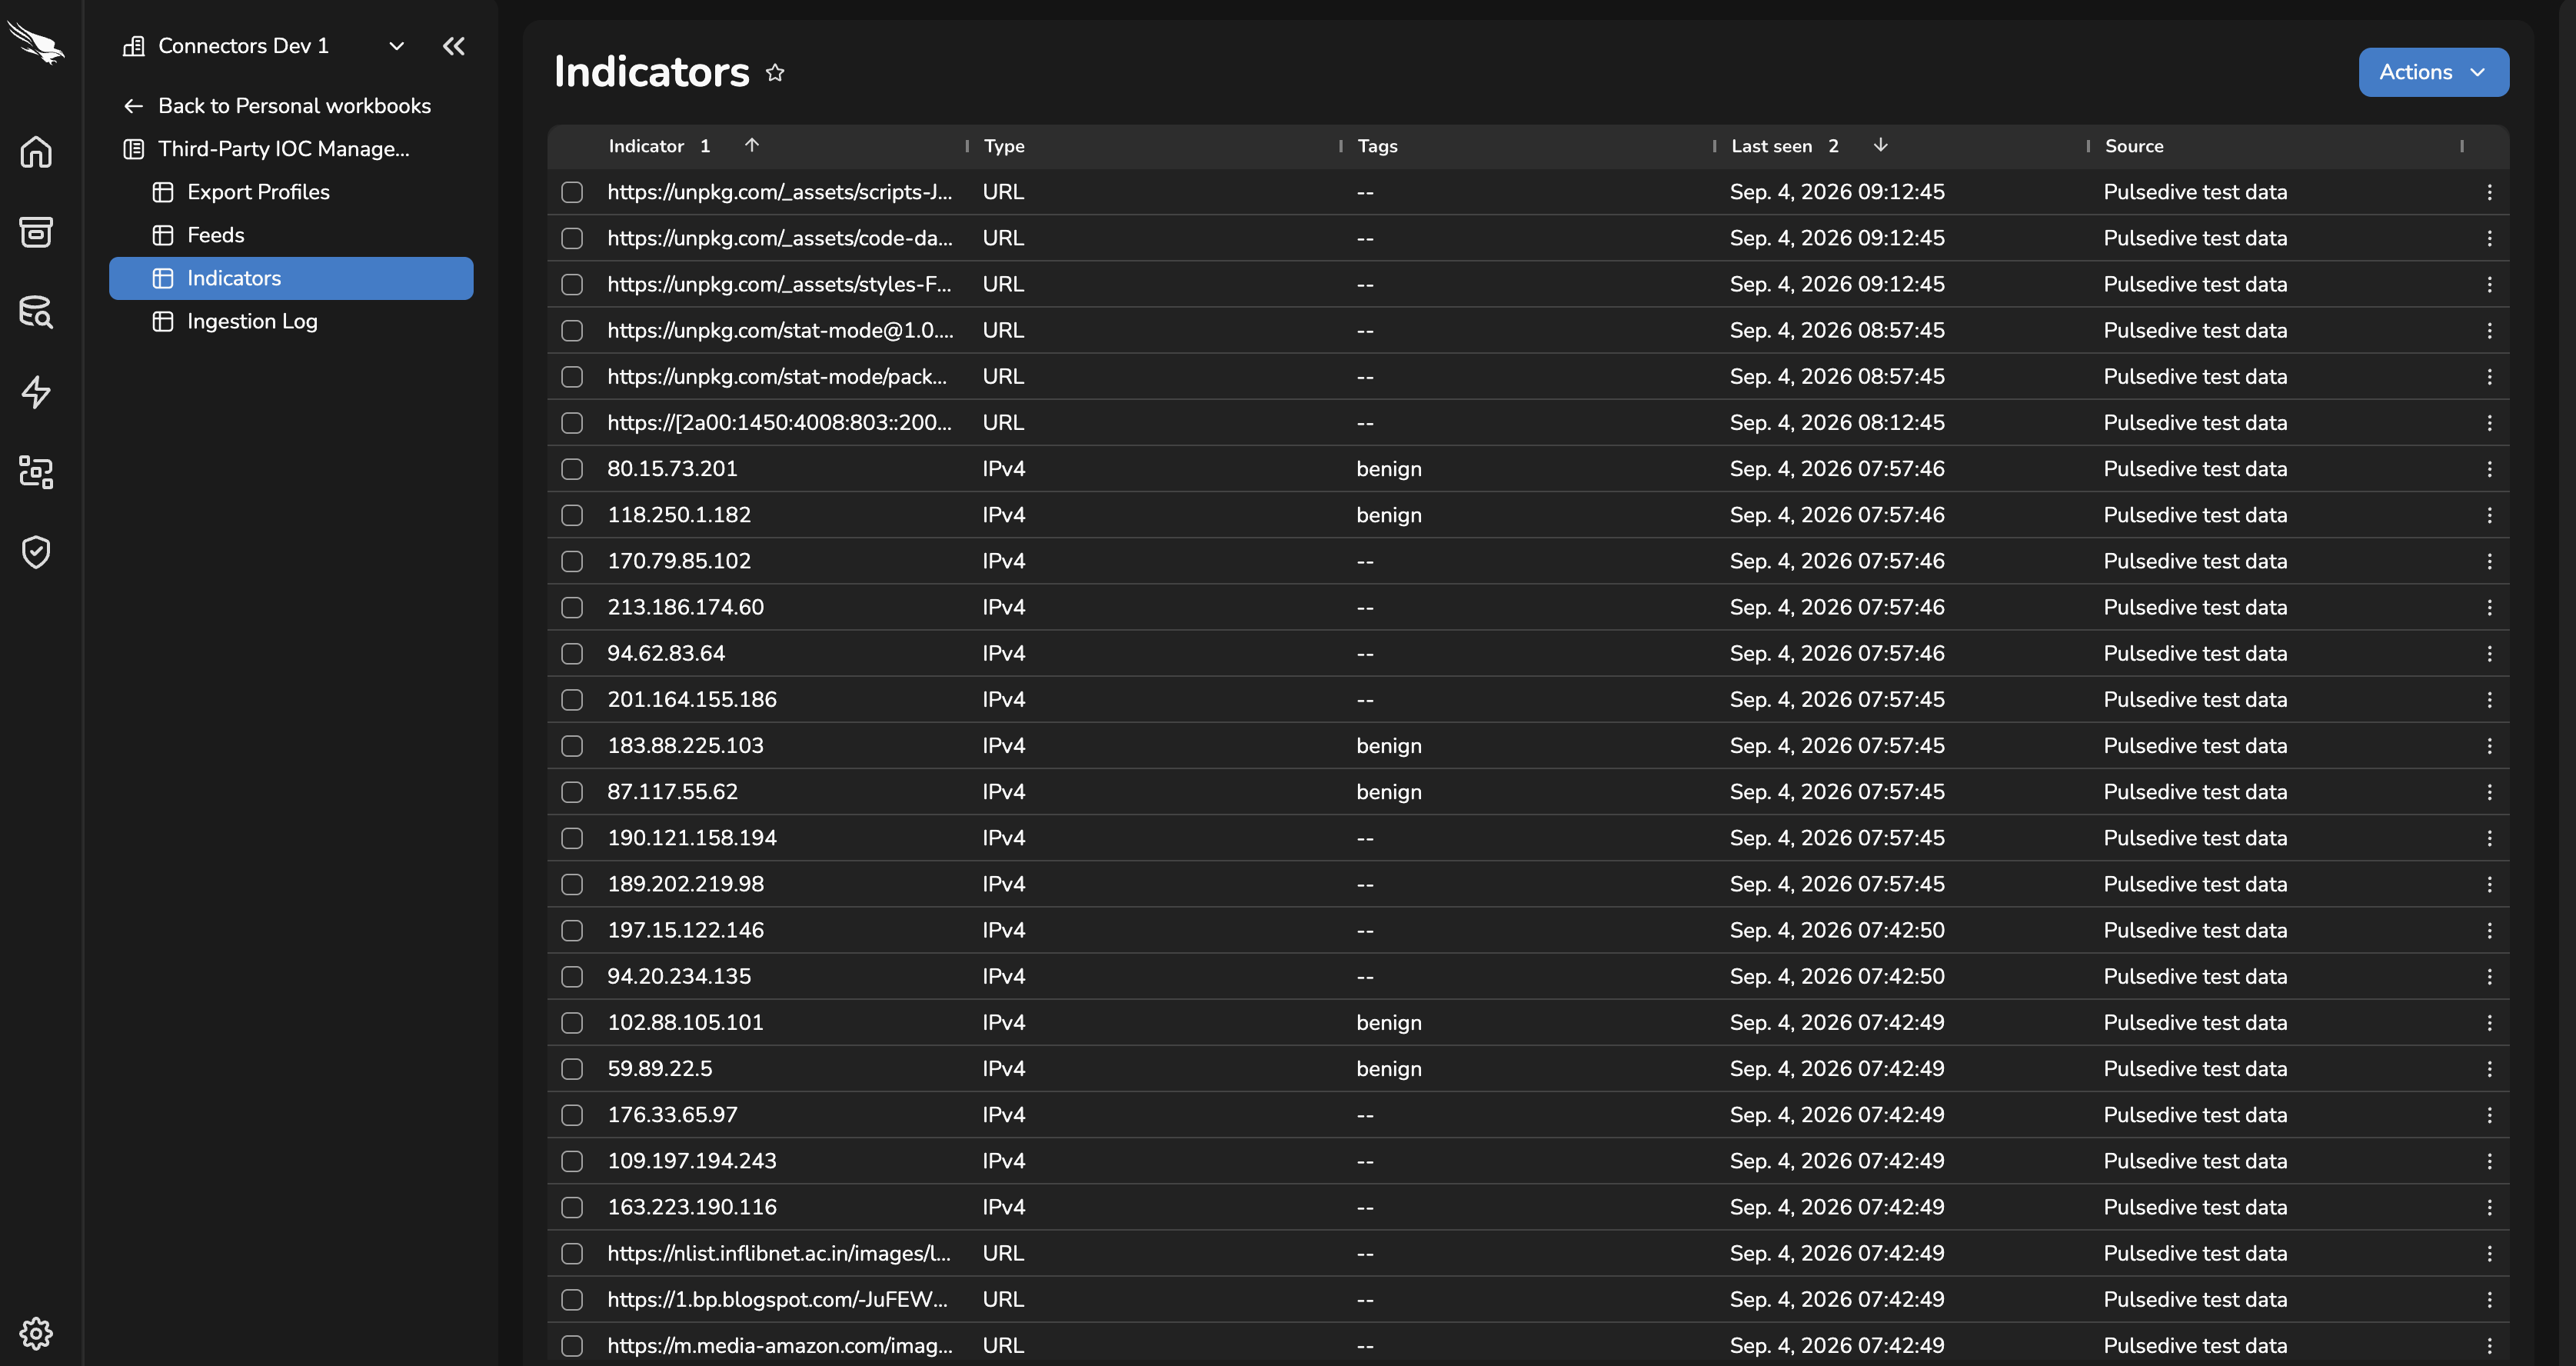
Enrich your detections with external threat intelligence by ingesting STIX indicators of compromise (IOCs) from any TAXII 2.0- or 2.1-compliant server into the CrowdStrike Falcon® platform. By centralizing IOC feeds within CrowdStrike Falcon® Next-Gen SIEM, your team can correlate third-party threat intelligence with endpoint and network telemetry, accelerate triage, and power custom detections against known-malicious file hashes, domains, IPs, and URLs.
- Centralize threat intelligence in Falcon Next-Gen SIEM
Ingest STIX indicators of compromise (IOCs) from any TAXII 2.0 or 2.1 server into CrowdStrike Falcon® Next-Gen SIEM to correlate external threat intelligence with endpoint, identity, and network telemetry for comprehensive threat visibility. - Accelerate triage and investigation
Leverage Falcon Next-Gen SIEM's built-in search, filtering, and timeline capabilities to rapidly correlate IOCs against your environment and investigate potential threats. - Power custom detections against known-malicious indicators
Match ingested file hashes, domains, IPs, and URLs against real-time telemetry to surface active threats and reduce mean time to detection.
Get Started
Easily ingest STIX threat-intelligence indicators of compromise (IOCs) from any TAXII 2.0 or 2.1 server into the CrowdStrike Falcon® platform
- Centralize threat intelligence in Falcon Next-Gen SIEM
- Accelerate triage and investigation
- Power custom detections against known-malicious indicators
Not A CrowdStrike Customer?
Try CrowdStrike


