Couldn’t make Fal.Con? Get in on Fal.Con Digital. Learn more


Your Cart
Added to Cart

There's nothing in your cart
per endpoint / per year
per endpoint / per month

×
![]()

×
![]()

×
![]()
×
![]()
- 01
- 02
- 03
- 04
- 05
Early and precise threat detection
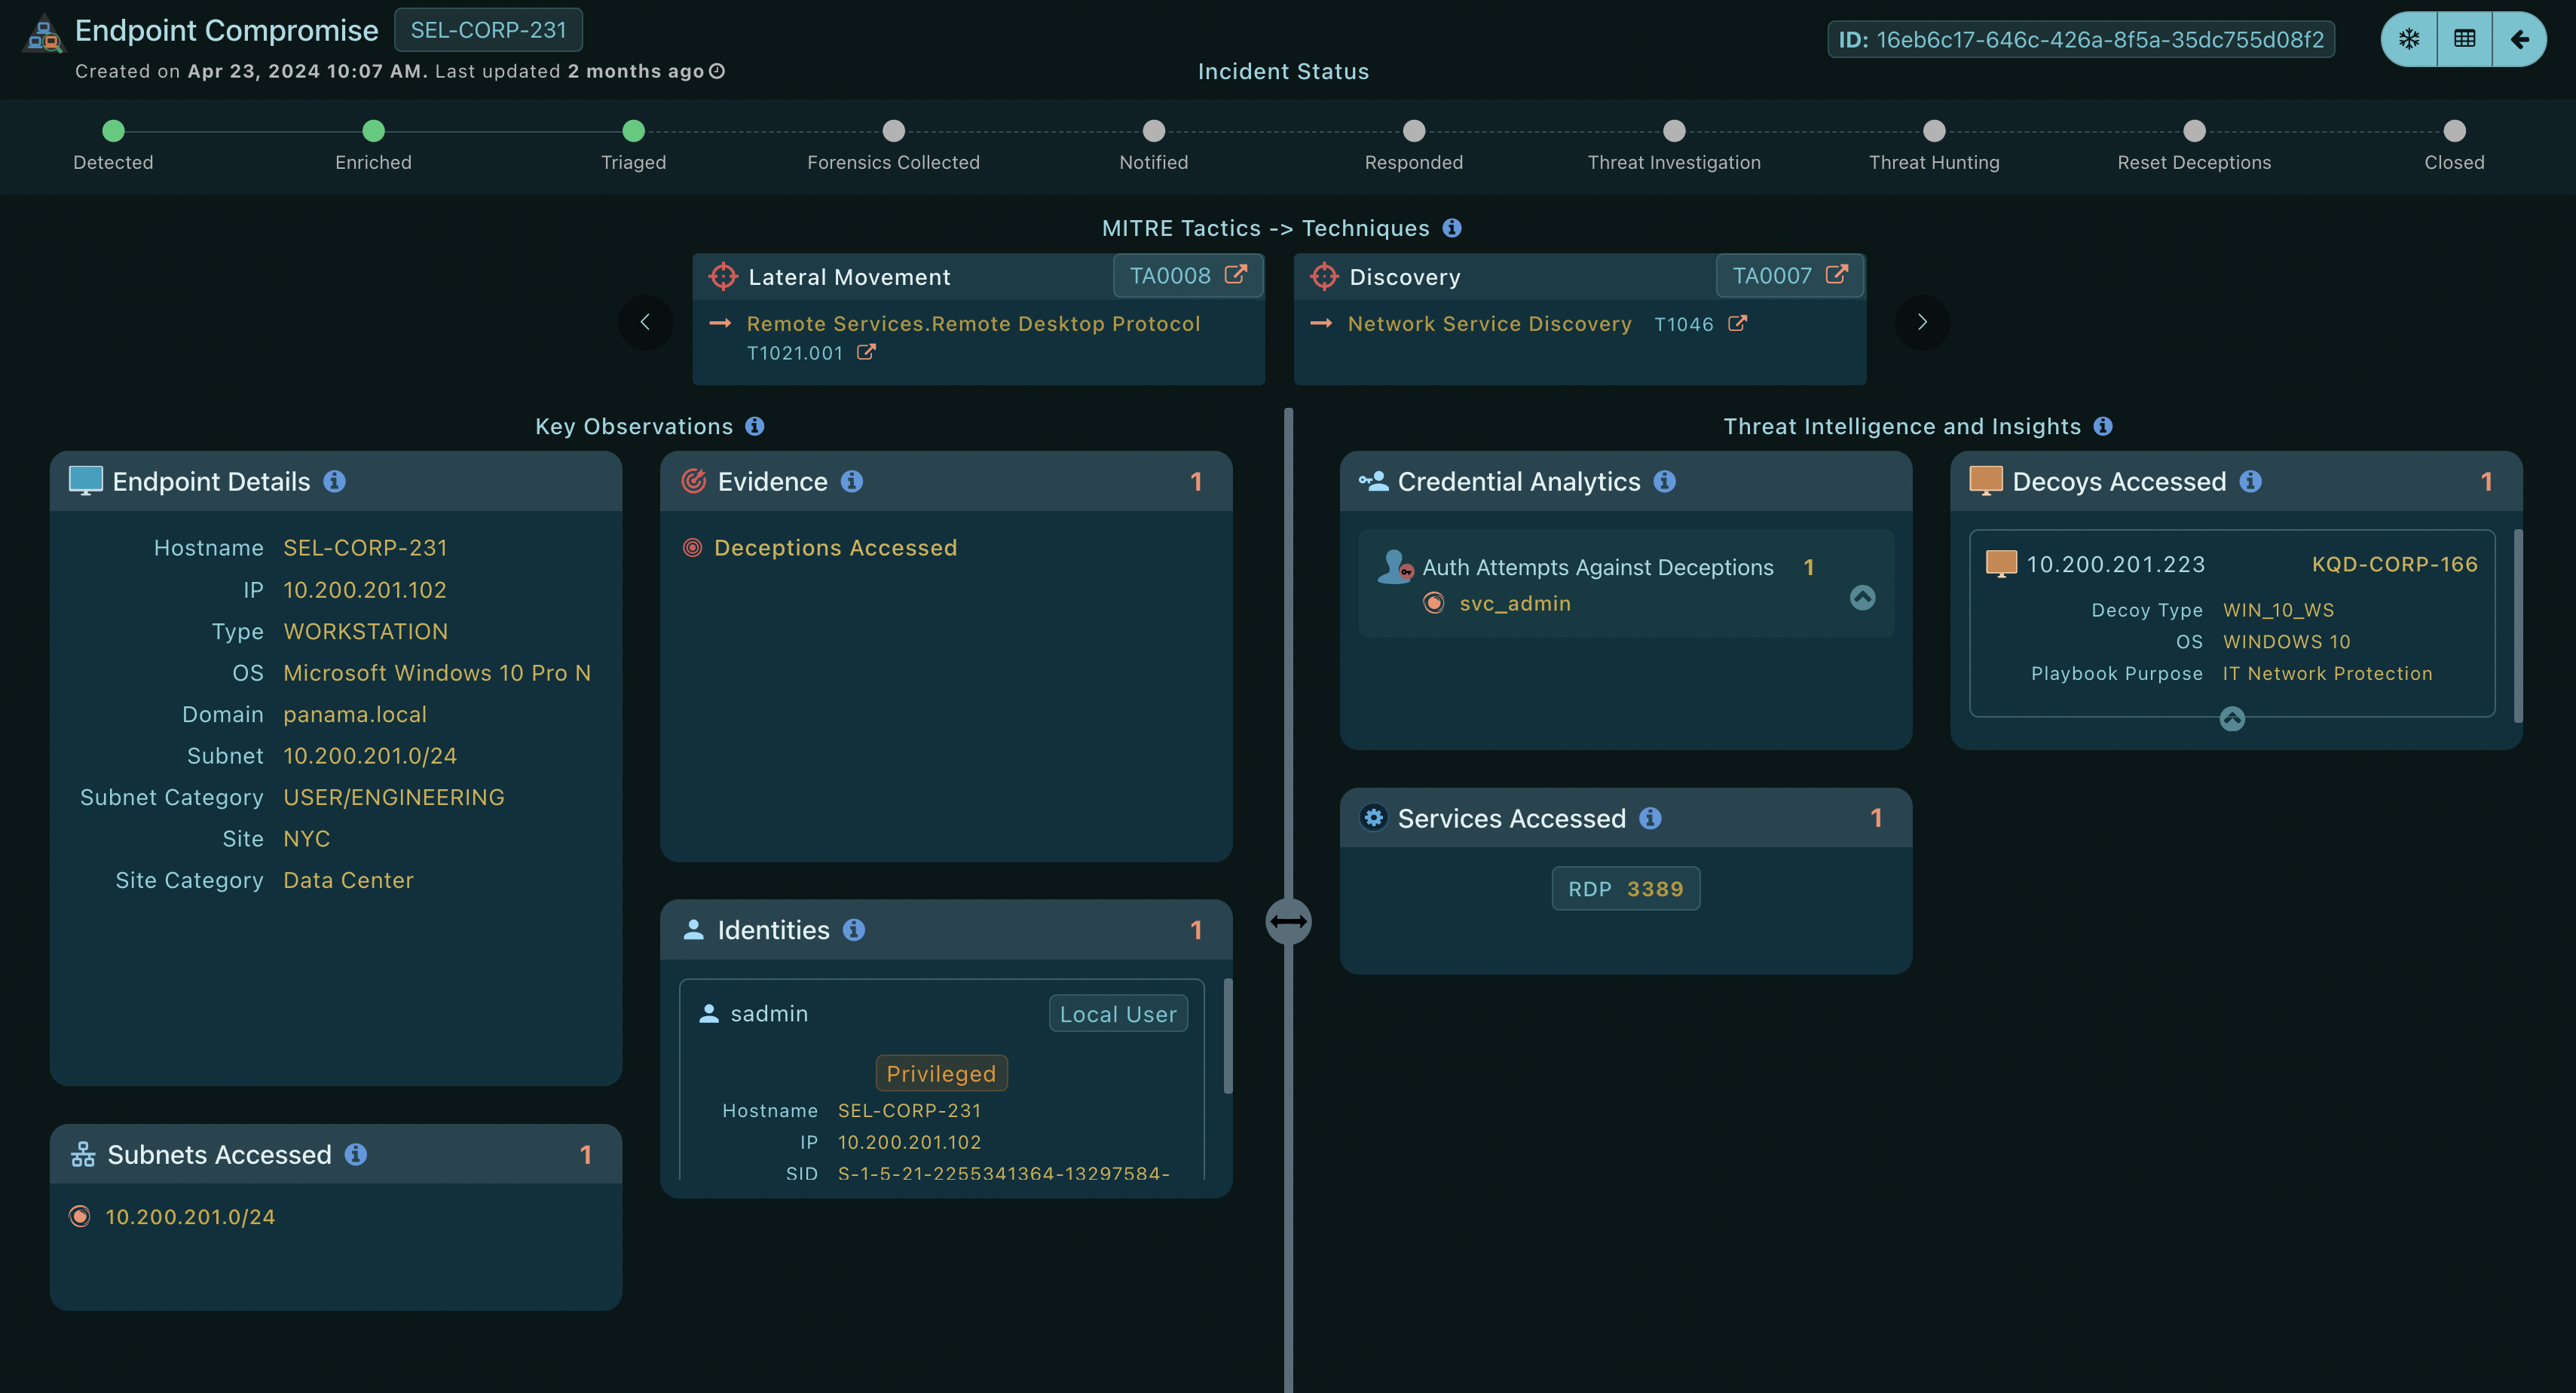
ShadowPlex integration with Falcon Endpoint enables enterprise-scale deception in an agentless deployment architecture. This enables ease of deployment of deception across the enterprise. The key integration points include:
- Early threat detection
Detect threats early in attack lifecycle to prevent adversary breakout - Insider threat detection
Detect accidental and privileged insider threats that evade traditional security - Advance Zero Trust Maturity
Improved cyber visibility for visibility and analytics - OT and IoT security
Detect threats targeting OT and IoT environments - Ransomware defense
Detect known and unknown ransomware threats with precision and speed - Active Threat hunting
Hypothesis testing and confirmation along with attacker TTP visibility through deception and analytics
Get Started
AI-Powered Cyber Deception to protect IT, OT, and Cloud
- Early threat detection
- Insider threat detection
- Advance Zero Trust Maturity
- OT and IoT security
- Ransomware defense
- Active Threat hunting
Not A CrowdStrike Customer?
Try CrowdStrike Falcon

