Couldn’t make Fal.Con? Get in on Fal.Con Digital. Learn more


Your Cart
Added to Cart

There's nothing in your cart
per endpoint / per year
per endpoint / per month
×
![]()
Accelerate operations and boost threat detection
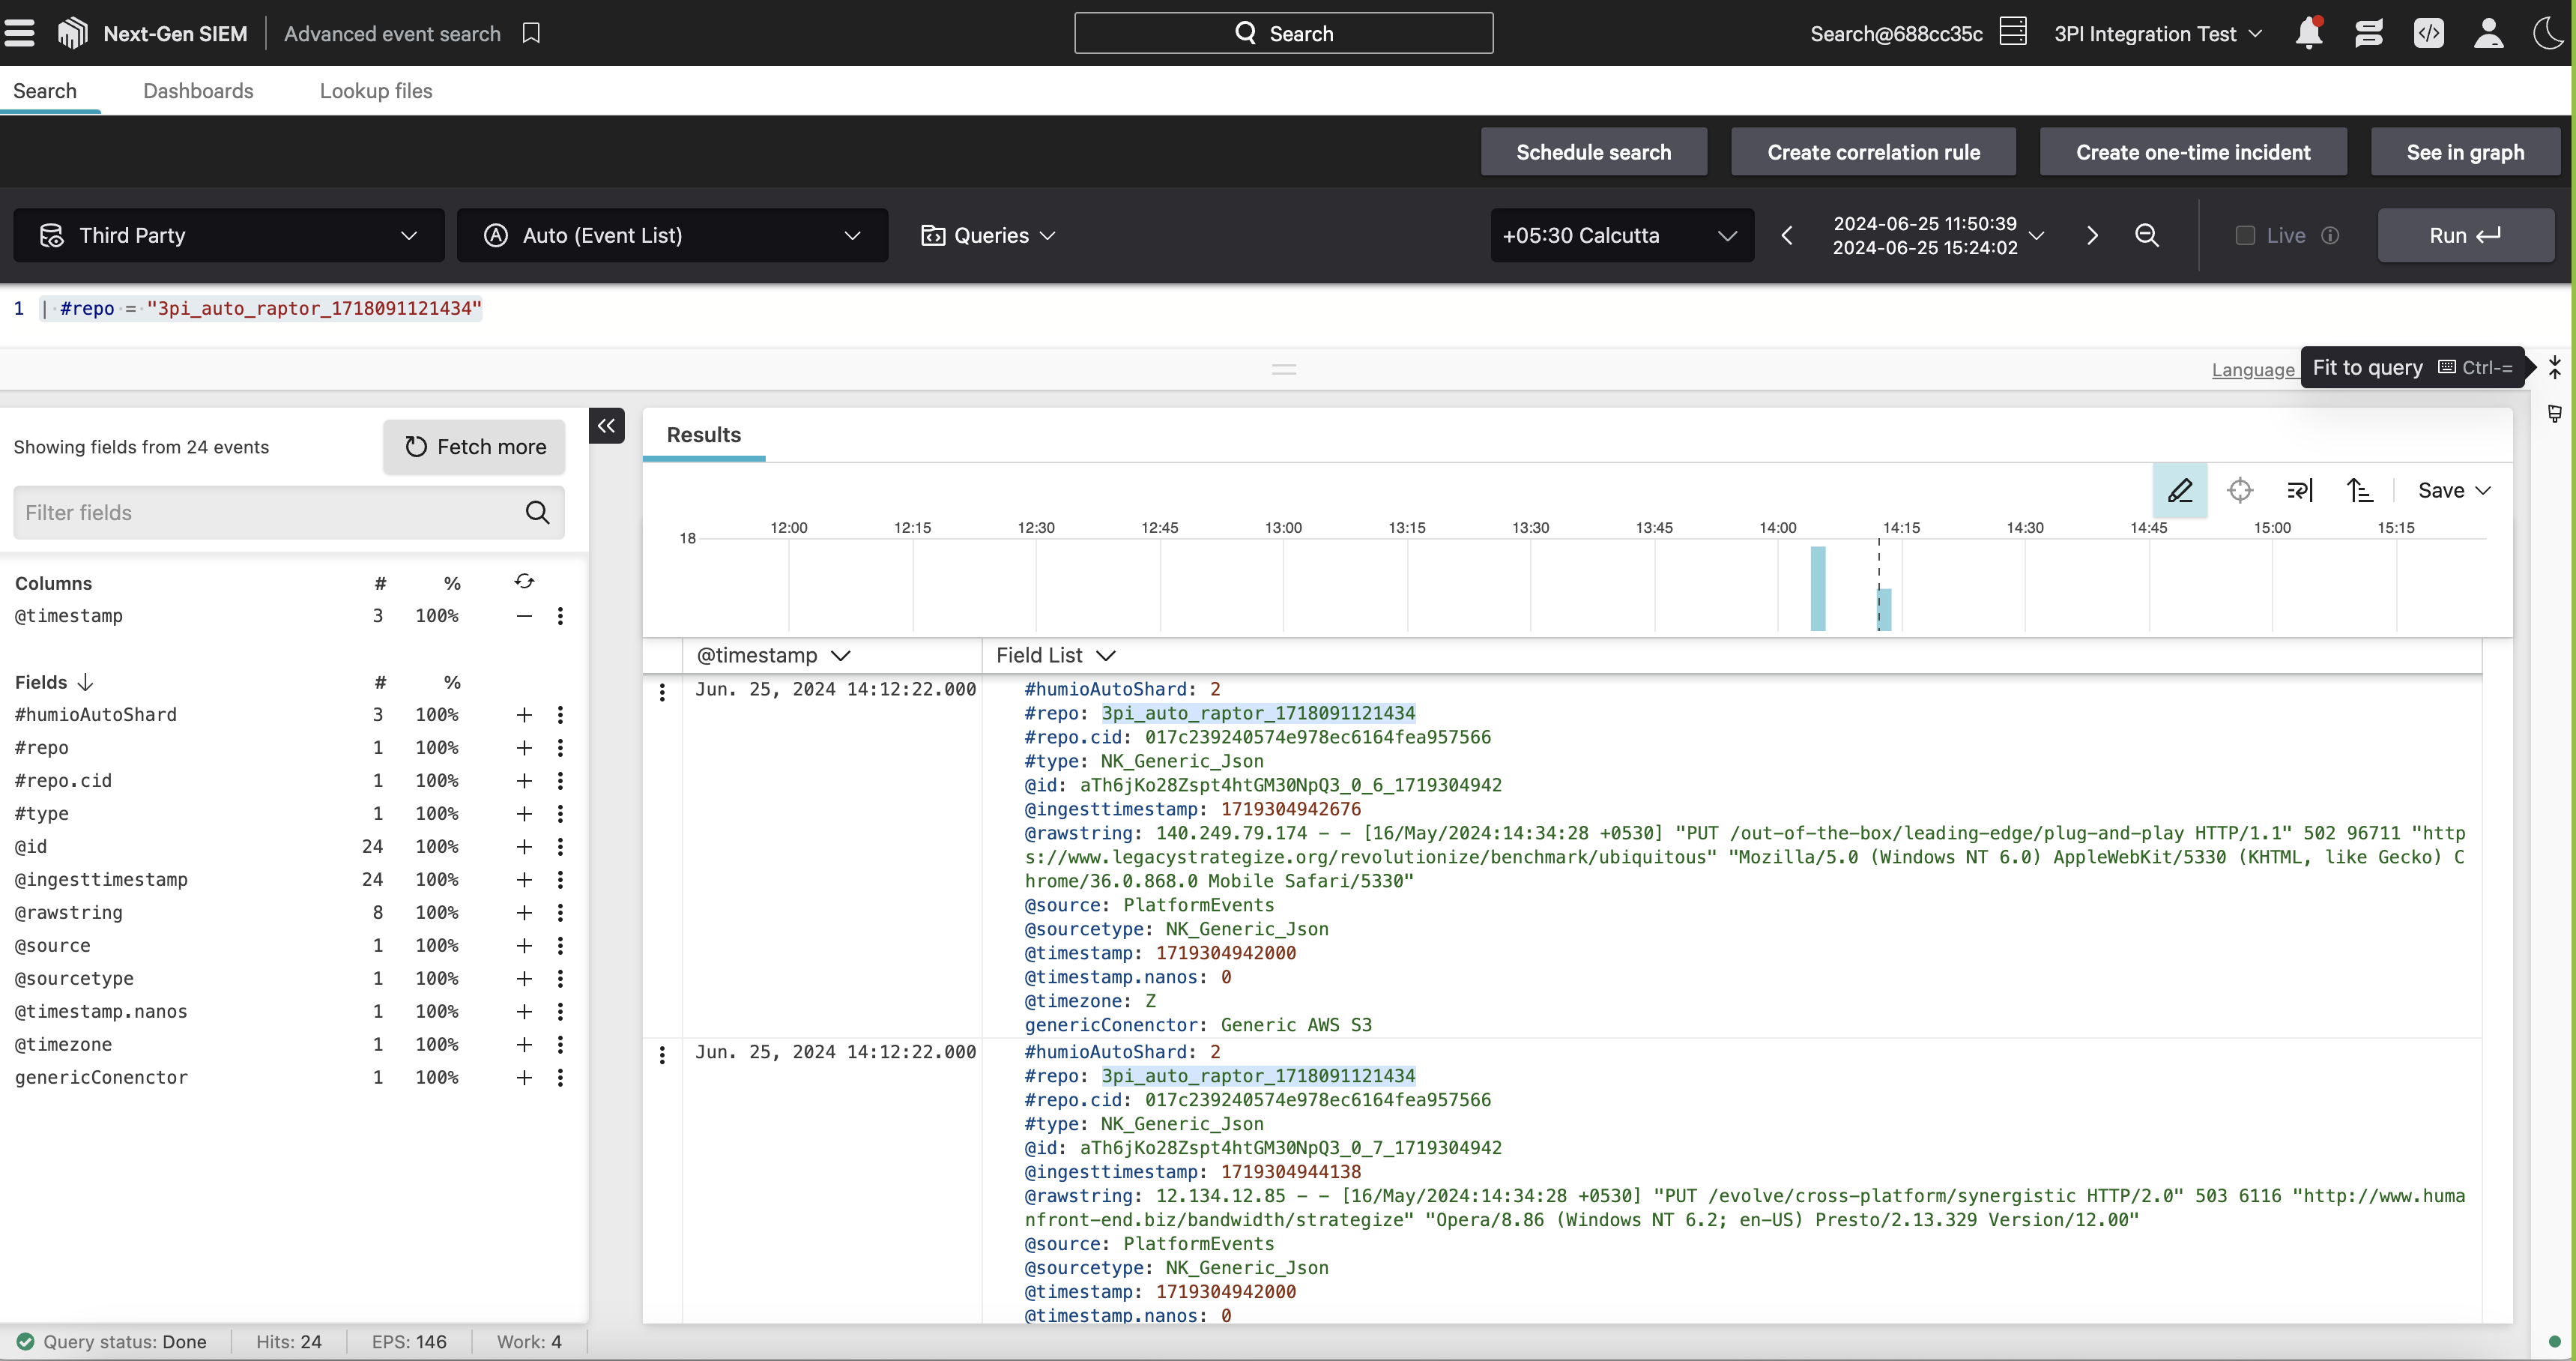
Secure your cloud infrastructure proactively and gain unified visibility by easily ingesting any security logs or events from an Amazon S3 bucket into the CrowdStrike Falcon platform using the generic S3 Data Connector. By centralizing and correlating powerful data and insights from logs and events collected from S3 bucket, the Falcon platform, and additional third parties via CrowdStrike Falcon Next-Gen SIEM, your team gains enhanced threat detection, streamlined incident response, and an optimized security posture to ultimately protect against evolving cyber threats.
- Enhance cloud threat detection
Gain an extensive view of your cloud environment and potential threats by analyzing security logs ingested from S3 that indicate potential malicious activity in to your AWS environment and correlating it with other security telemetry within the Falcon platform - Streamline investigations and incident response
Accelerate response with detailed timelines of events and actionable forensic data from security logs ingested from S3, using built-in search and filtering capabilities from Falcon Next-Gen SIEM - Improve threat hunting
Store and correlate your security data with other data sources in the Falcon platform for real-time detections and agile search to rapidly shut down threats
Get Started
Easily ingest any security logs or events from Amazon S3 into the CrowdStrike Falcon platform
- Enhance cloud threat detection
- Streamline investigations and incident response
- Improve threat hunting
Not A CrowdStrike Customer?
Try CrowdStrikeSupport


