Couldn’t make Fal.Con? Get in on Fal.Con Digital. Learn more


Your Cart
Added to Cart

There's nothing in your cart
per endpoint / per year
per endpoint / per month

×
![]()
×
![]()
×
![]()
×
![]()
- 01
- 02
- 03
- 04
- 05
A complete industrial cybersecurity solution
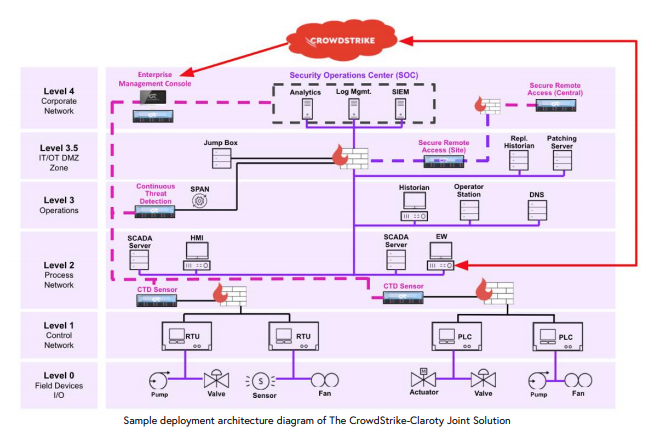
By combining the endpoint you rely on from CrowdStrike Falcon® with Claroty‘s OT visibility and monitoring, you can efficiently detect and address threats, while overseeing all IT and OT assets in one place.
- Improved detection of threats crossing the IT/OT boundary
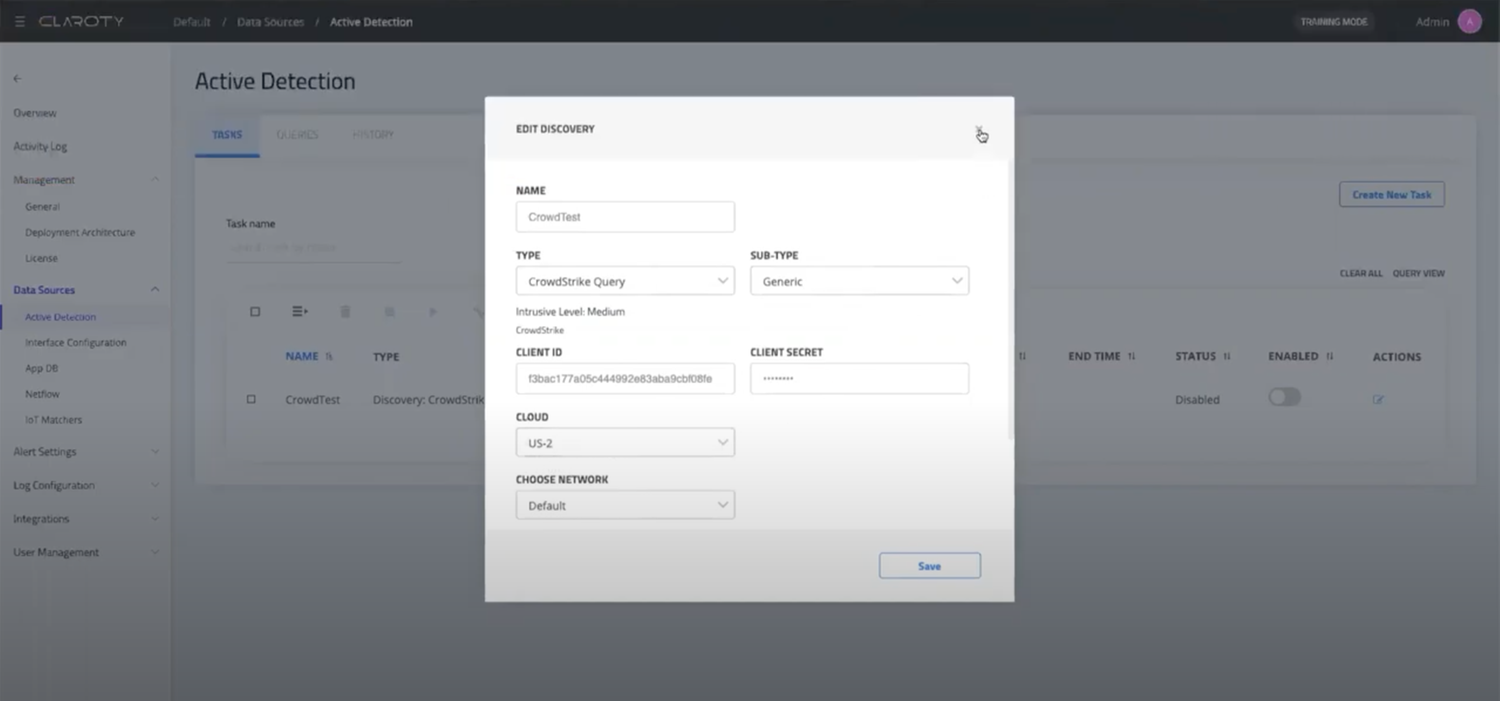
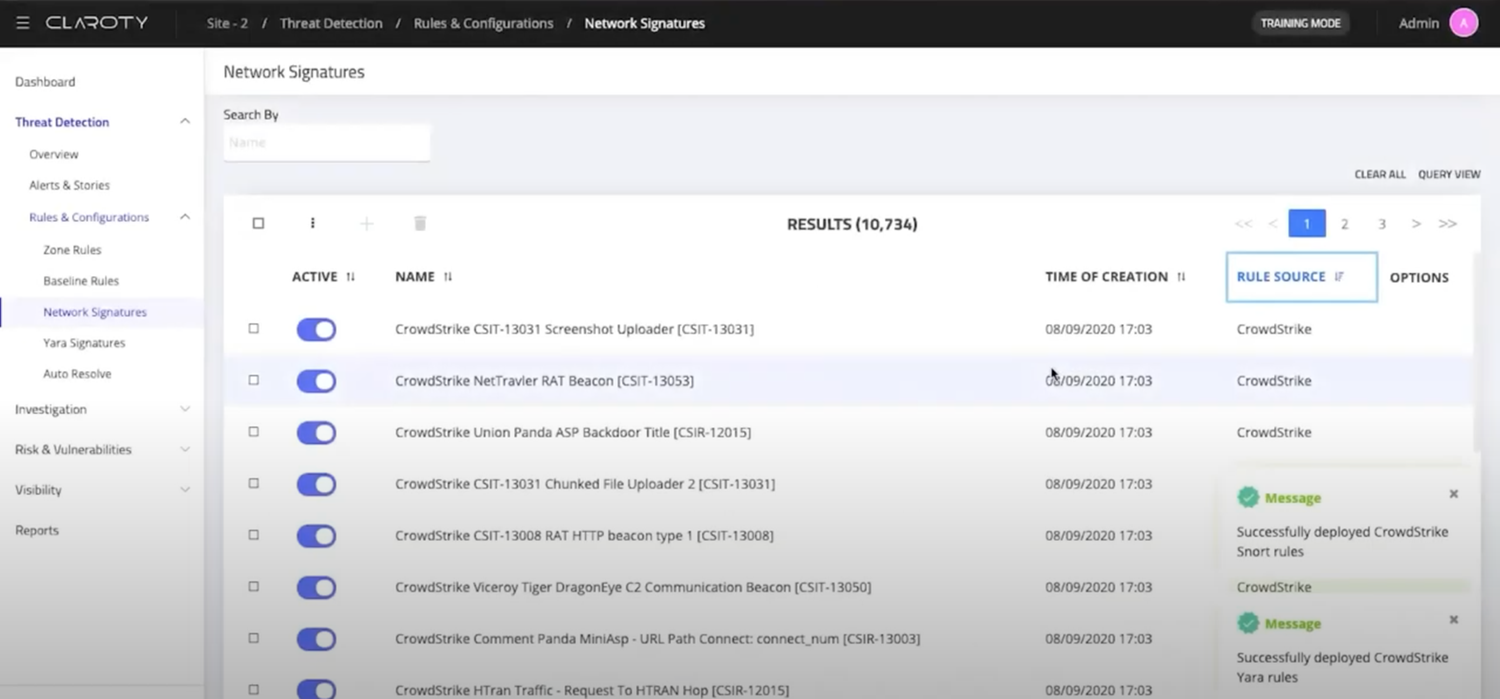
Claroty integrates CrowdStrike‘s endpoint monitoring with OT visibility within Claroty‘s platform to deliver the industry‘s largest IT/OT threat signature database, combining YARA and Snort rules from both companies for industrial network security - Unified visibility of IT/OT assets across connected sites
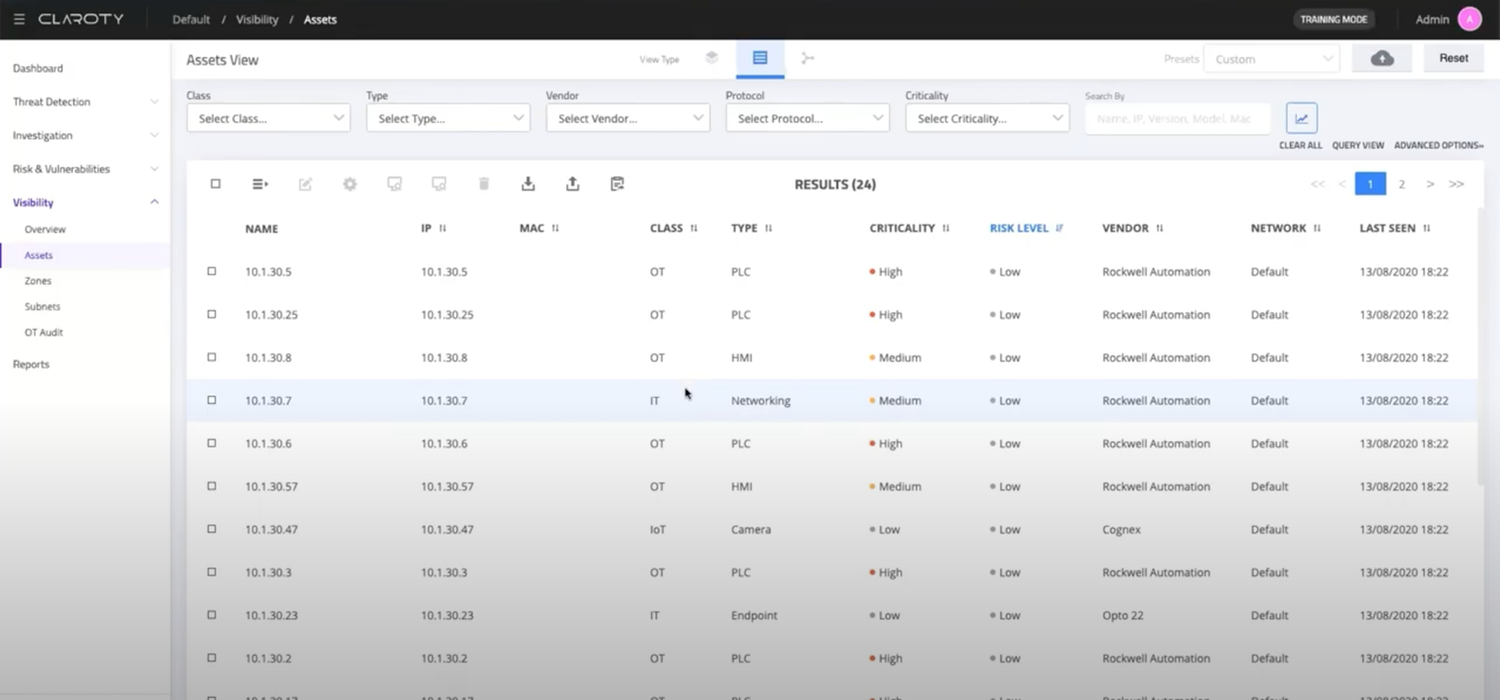
By merging CrowdStrike‘s endpoint data with Claroty‘s network visibility, you can automatically identify and enrich IT-oriented industrial assets where a CrowdStrike agent is installed, including those in an OT environment - CrowdStrike + Claroty = Increased ROI
The joint solution enhances both platforms, making their insights readily usable. This expanded visibility across IT and OT environments improves resource use and streamlines investigation and remediation
Get Started
Unmatched visibility and protection for OT, IoT, IoMT, and IT assets
- Improved detection of threats crossing the IT/OT boundary
- Unified visibility of IT/OT assets across connected sites
- CrowdStrike + Claroty = Increased ROI
Not A CrowdStrike Customer?
Try CrowdStrike


