Discover the latest news and innovations from Fal.Con Europe Learn more


Your Cart
Added to Cart

There's nothing in your cart
per endpoint / per year
per endpoint / per month
×
![]()
Accelerate operations and boost threat detection
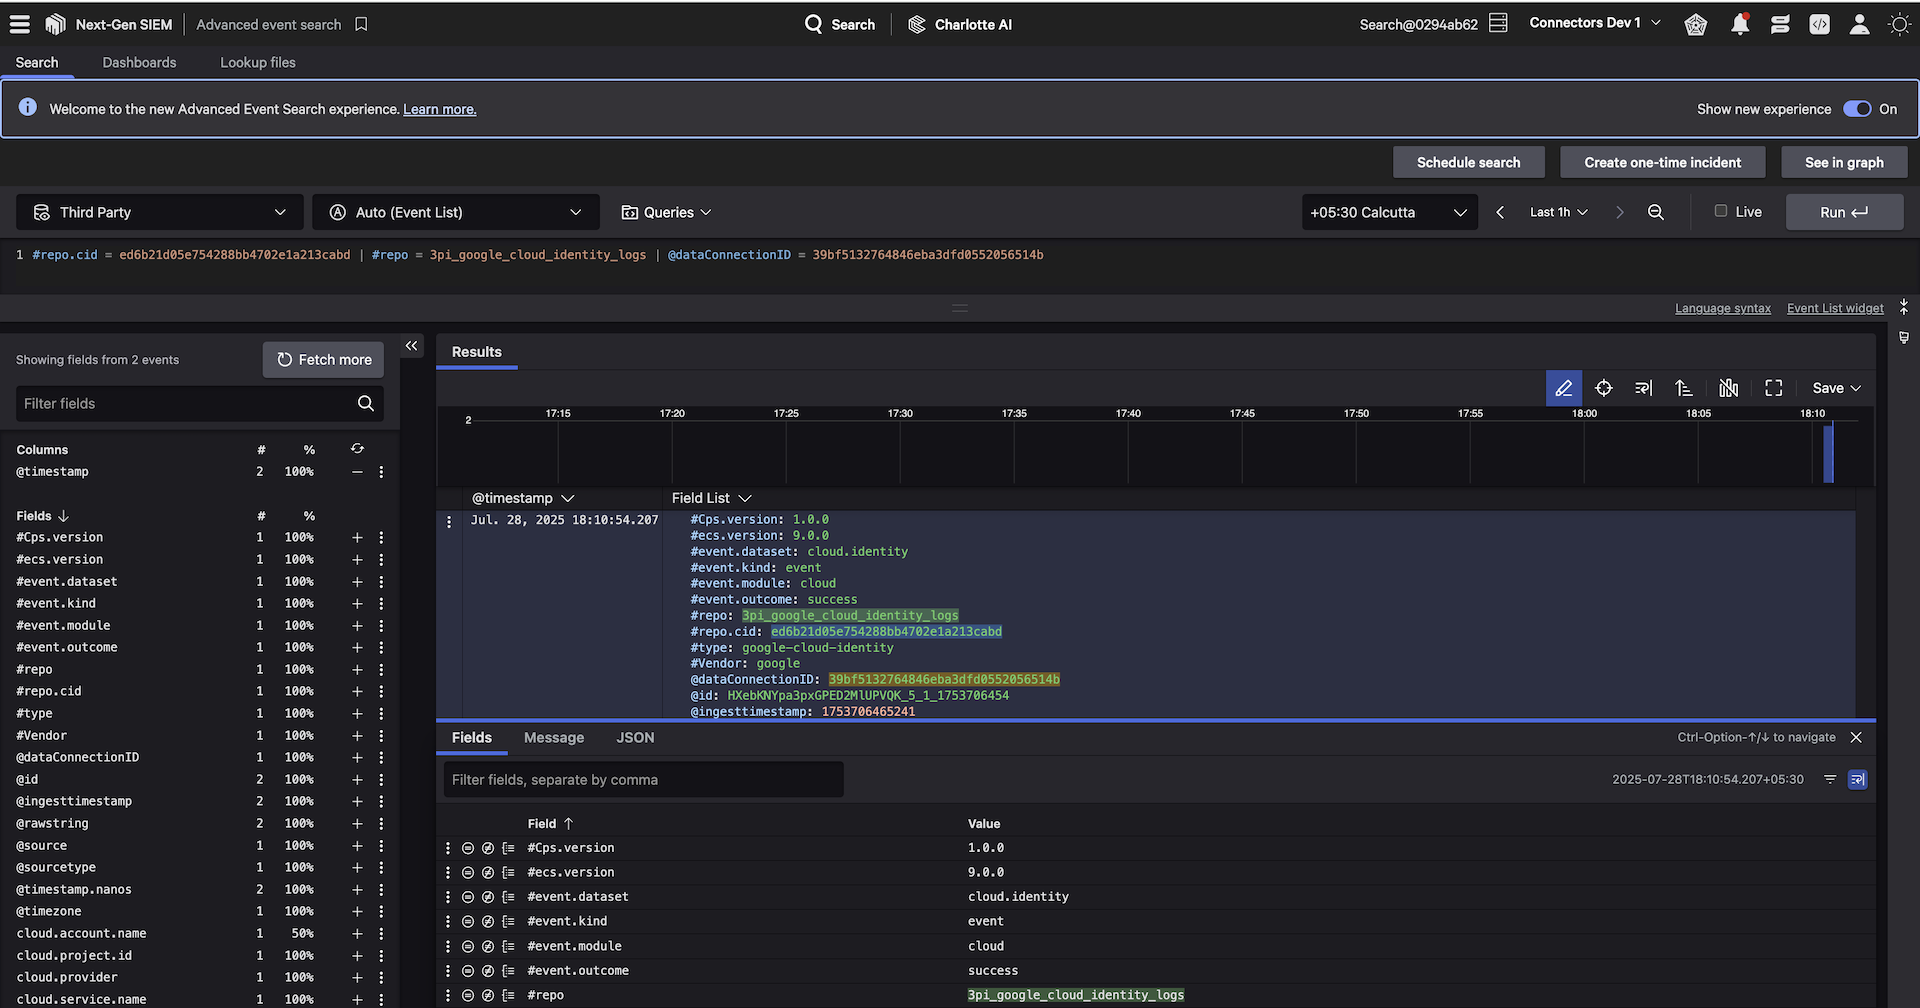
Enhance your identity security monitoring by seamlessly ingesting Google Cloud Identity Platform logs into the CrowdStrike Falcon® platform. This integration provides comprehensive visibility into authentication events, user activities, and identity-related security incidents across your Google Cloud environment. By centralizing authentication logs within Falcon® Next-Gen SIEM, security teams can effectively monitor access patterns, detect suspicious authentication attempts, and respond rapidly to identity-based threats.
- Unify threat visibility in a single console
Save your analysts valuable time when investigating and triaging potential threats by minimizing context switching through CrowdStrike’s unified, threat-centric command console. - Simplify data ingestion
Easily ingest third party data with the new Falcon Data Connectors user interface. Get full visibility into your data ingestion pipeline and see all connectors with their corresponding status. - Improve threat hunting
Store and correlate your security data with other data sources leveraging the Falcon platform as a destination, including real-time detections and blazing-fast search to rapidly shut down threats.
Get Started
Easily ingest Google Cloud Identity Platform logs and events into the CrowdStrike Falcon® platform
- Unify threat visibility in a single console
- Simplify data ingestion
- Improve threat hunting
Not A CrowdStrike Customer?
Try CrowdStrikeSupport


