Couldn’t make Fal.Con? Get in on Fal.Con Digital. Learn more


Your Cart
Added to Cart

There's nothing in your cart
per endpoint / per year
per endpoint / per month

×
![]()
×
![]()
×
![]()
×
![]()
- 01
- 02
- 03
- 04
Empower security teams with CrowdStrike + Splunk
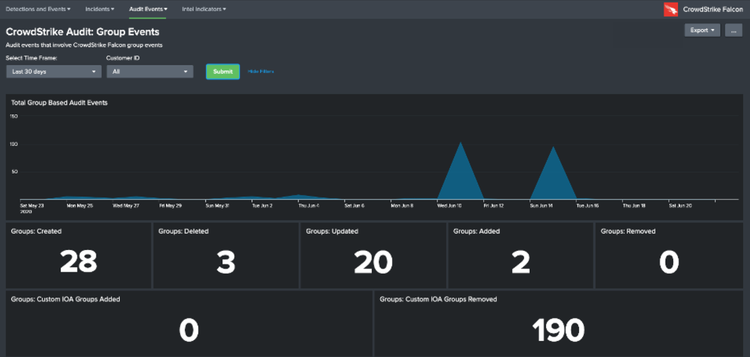
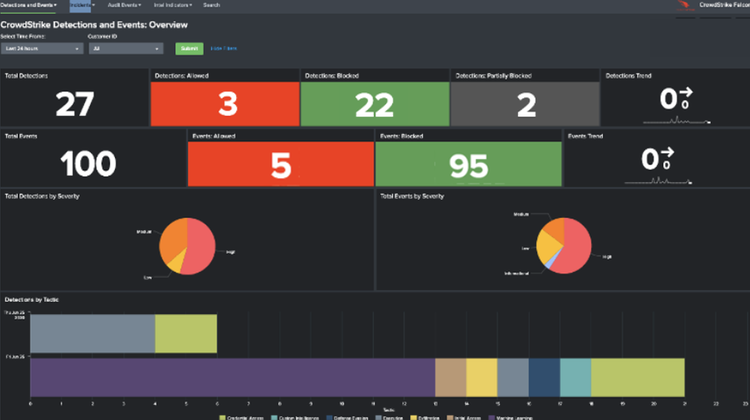
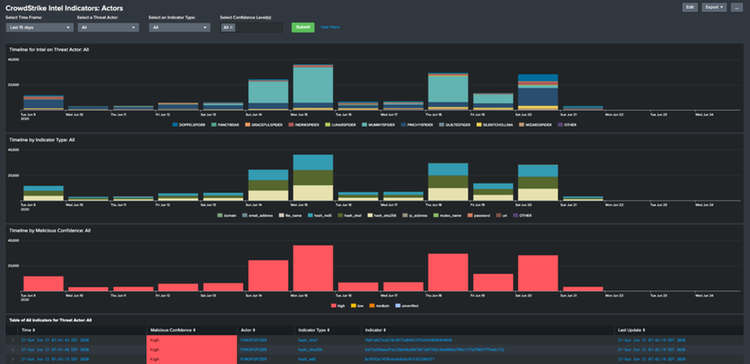
CrowdStrike and Splunk enhance security teams with concise insights for more efficient and accurate work. The Splunk and CrowdStrike integrations deliver rich visualizations and drill-downs for CrowdStrike data, and the ability to manage indicators of compromise (IOCs) for enhanced investigations.
- Correlate data
Correlate CrowdStrike Falcon® detections to create notable events in Splunk Enterprise Security to identify trends and prioritize threats - Get better visibility
Quickly and easily combine CrowdStrike intelligence with all other machine data into Splunk for better visibility - Stop attacks faster
Integrate threat detections to enable security analyst to stop attacks faster - Insight to empower security teams
Get the context and intelligence needed to empower security teams to work smarter, faster and with more accuracy
Get Started
Insight to empower security teams
- Correlate data
- Get better visibility
- Stop attacks faster
- Insight to empower security teams
Not A CrowdStrike Customer?
Try CrowdStrikeDetails
Built by
SplunkCategories
IT and Security Operations Security AnalyticsRequirements
Falcon Insight XDR Falcon Prevent Falcon IntelligenceSupport
Documents


